
Malware Forensic Analysis: Capturing What Attackers Leave Behind
Container attacks vanish fast—before you even detect them.
 Lucifer DDoS botnet Malware is Targeting Apache Big-Data StackAquasec
 Gafgyt Malware Variant Exploits GPU Power and Cloud Native EnvironmentsAquasec
 Detecting and Capturing Kernel Modules with Tracee and eBPFAquasec
 PG_MEM: A Malware Hidden in the Postgres ProcessesAquasec
 Tracee Release: Rules Detect Attackers Out-of-the-BoxAquasec
 New npm Flaws Let Attackers Better Target Packages for Account TakeoverAquasec
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 Breaking down common documentation mistakesMintlify
 Who Explains the Most? An Analysis of Educational YouTubers - Deepgram Blog ⚡️Deepgram
 How a top tier European soccer team sped up their data processing and reduced costs by 50%Modal
 Capturing Logs in Docker DesktopDocker
 Collaborate in the editor - MintlifyMintlify
 How to Build Real-Time Sentiment Analysis for Streaming AudioDeepgram
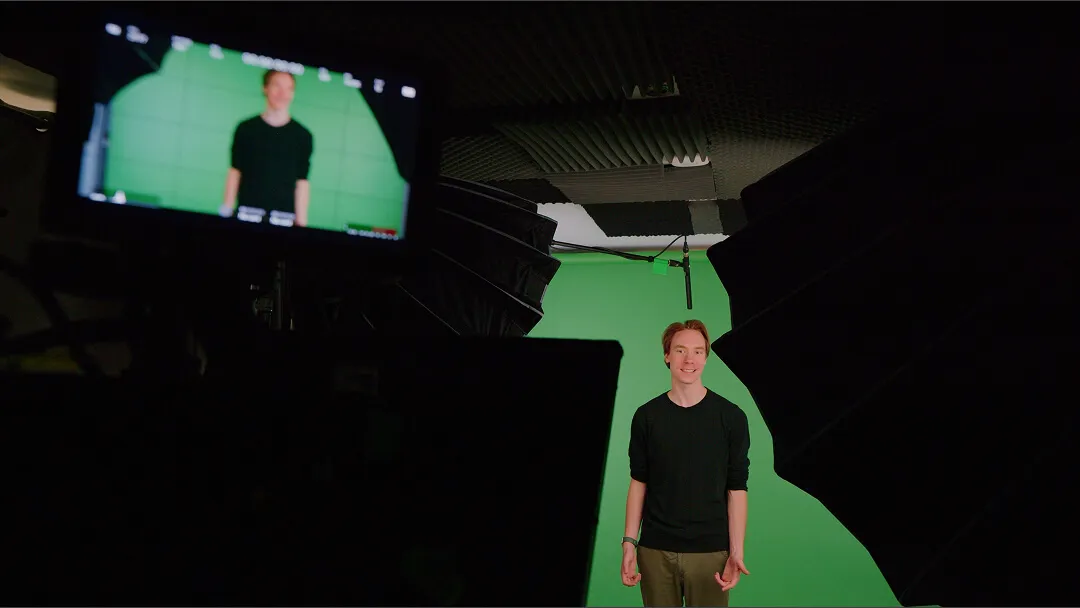 Synthesia launches talent experience program to learn from and reward the exceptional actors behindSynthesia
 Anthropic Identifies Biased Reasoning and Recklessness as Drivers of Claude’s PyPI AttackSocket
 Comparing Reachability Analysis ProvidersSocket
 The Coana Approach to Reachability AnalysisSocket
 Be the Hero in Your Real-Life Cyber Heist ScriptThenewstack
 Siloscape: Windows Malware That Breaks KubernetesThenewstack
 What is Root Cause Analysis?Datadoghq
