
Supply Chain Security Risk: GitHub Action tj-actions/changed-files Compromised
CVE-2024-29029 allow malicious code injection in a popular GitHub Action potentially exposing secrets.
 A Brief Guide to Supply Chain Security Best PracticesAquasec
 Empowering Security: Bridging Talk to Action at RSA 2024Aquasec
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Aqua and HashiCorp Enable Cloud Native Security, Zero-Trust ApproachesAquasec
 Cloud VM Security with Aqua CSPAquasec
 Istio Security: Zero-Trust NetworkingAquasec
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 Looping by Zapier: Repeat actions for itemsZapier
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Integrate Jupyter Notebooks with GitHubThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Pulumi Neo Now Supports AGENTS.mdPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
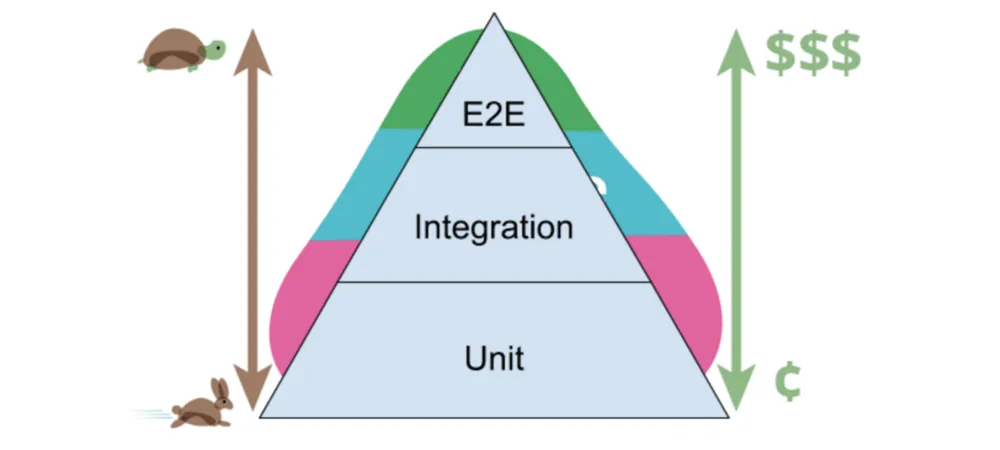 Develop, Preview, TestCss Tricks
 Analyze JSON Data Using SQL and DuckDBMotherduck
