
Trivy Image Vulnerability Scanner Now Under Apache 2.0 License
Trivy, the open source image vulnerability scanner is now under Apache 2.0 license, allowing a wider usage beyond Harbor and Docker Enterprise registries.
 Trivy: The Universal Scanner to Secure Your Cloud MigrationAquasec
 Sink or Swim: Tackling 2024's Record-Breaking Vulnerability WaveAquasec
 Looney Tunables Vulnerability Exploited by KinsingAquasec
 Lucifer DDoS botnet Malware is Targeting Apache Big-Data StackAquasec
 Vulnerability Management in Container ImagesAquasec
 Cloud Native Security Best Practices: Vulnerability ManagementAquasec
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Grafana Is Not Worried About AWS CommercializationThenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
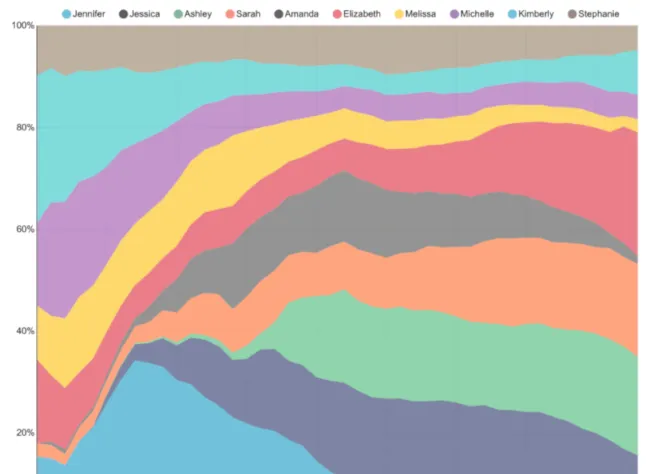 Explore and Visualize Data the Apache Superset WayThenewstack
 Pulumi ESC Table Editor Now Supports Dynamic Credential and Secret IntegrationsPulumi
 Discovered Stacks: One Place for All Your InfrastructurePulumi
 Pulumi Neo Now Supports AGENTS.mdPulumi
 New Policy as Code Capabilities with CrossGuardPulumi
 The Go Memory Model - The Go Programming LanguageGo
 How Hunch supercharged AI workflows with Modal SandboxesModal
 Modal SDKs for JavaScript and Go (alpha)Modal
 The Serverless Backend for Analytics: Introducing MotherDuck’s Native Integration on VercelMotherduck
 Docker Desktop 4.23: Updates to Docker Init, New Configuration Integrity Check, Quick SearchDocker
 How to Use AI Image to Video Generator for Free to Create Dynamic VideosHeygen
