Blogs
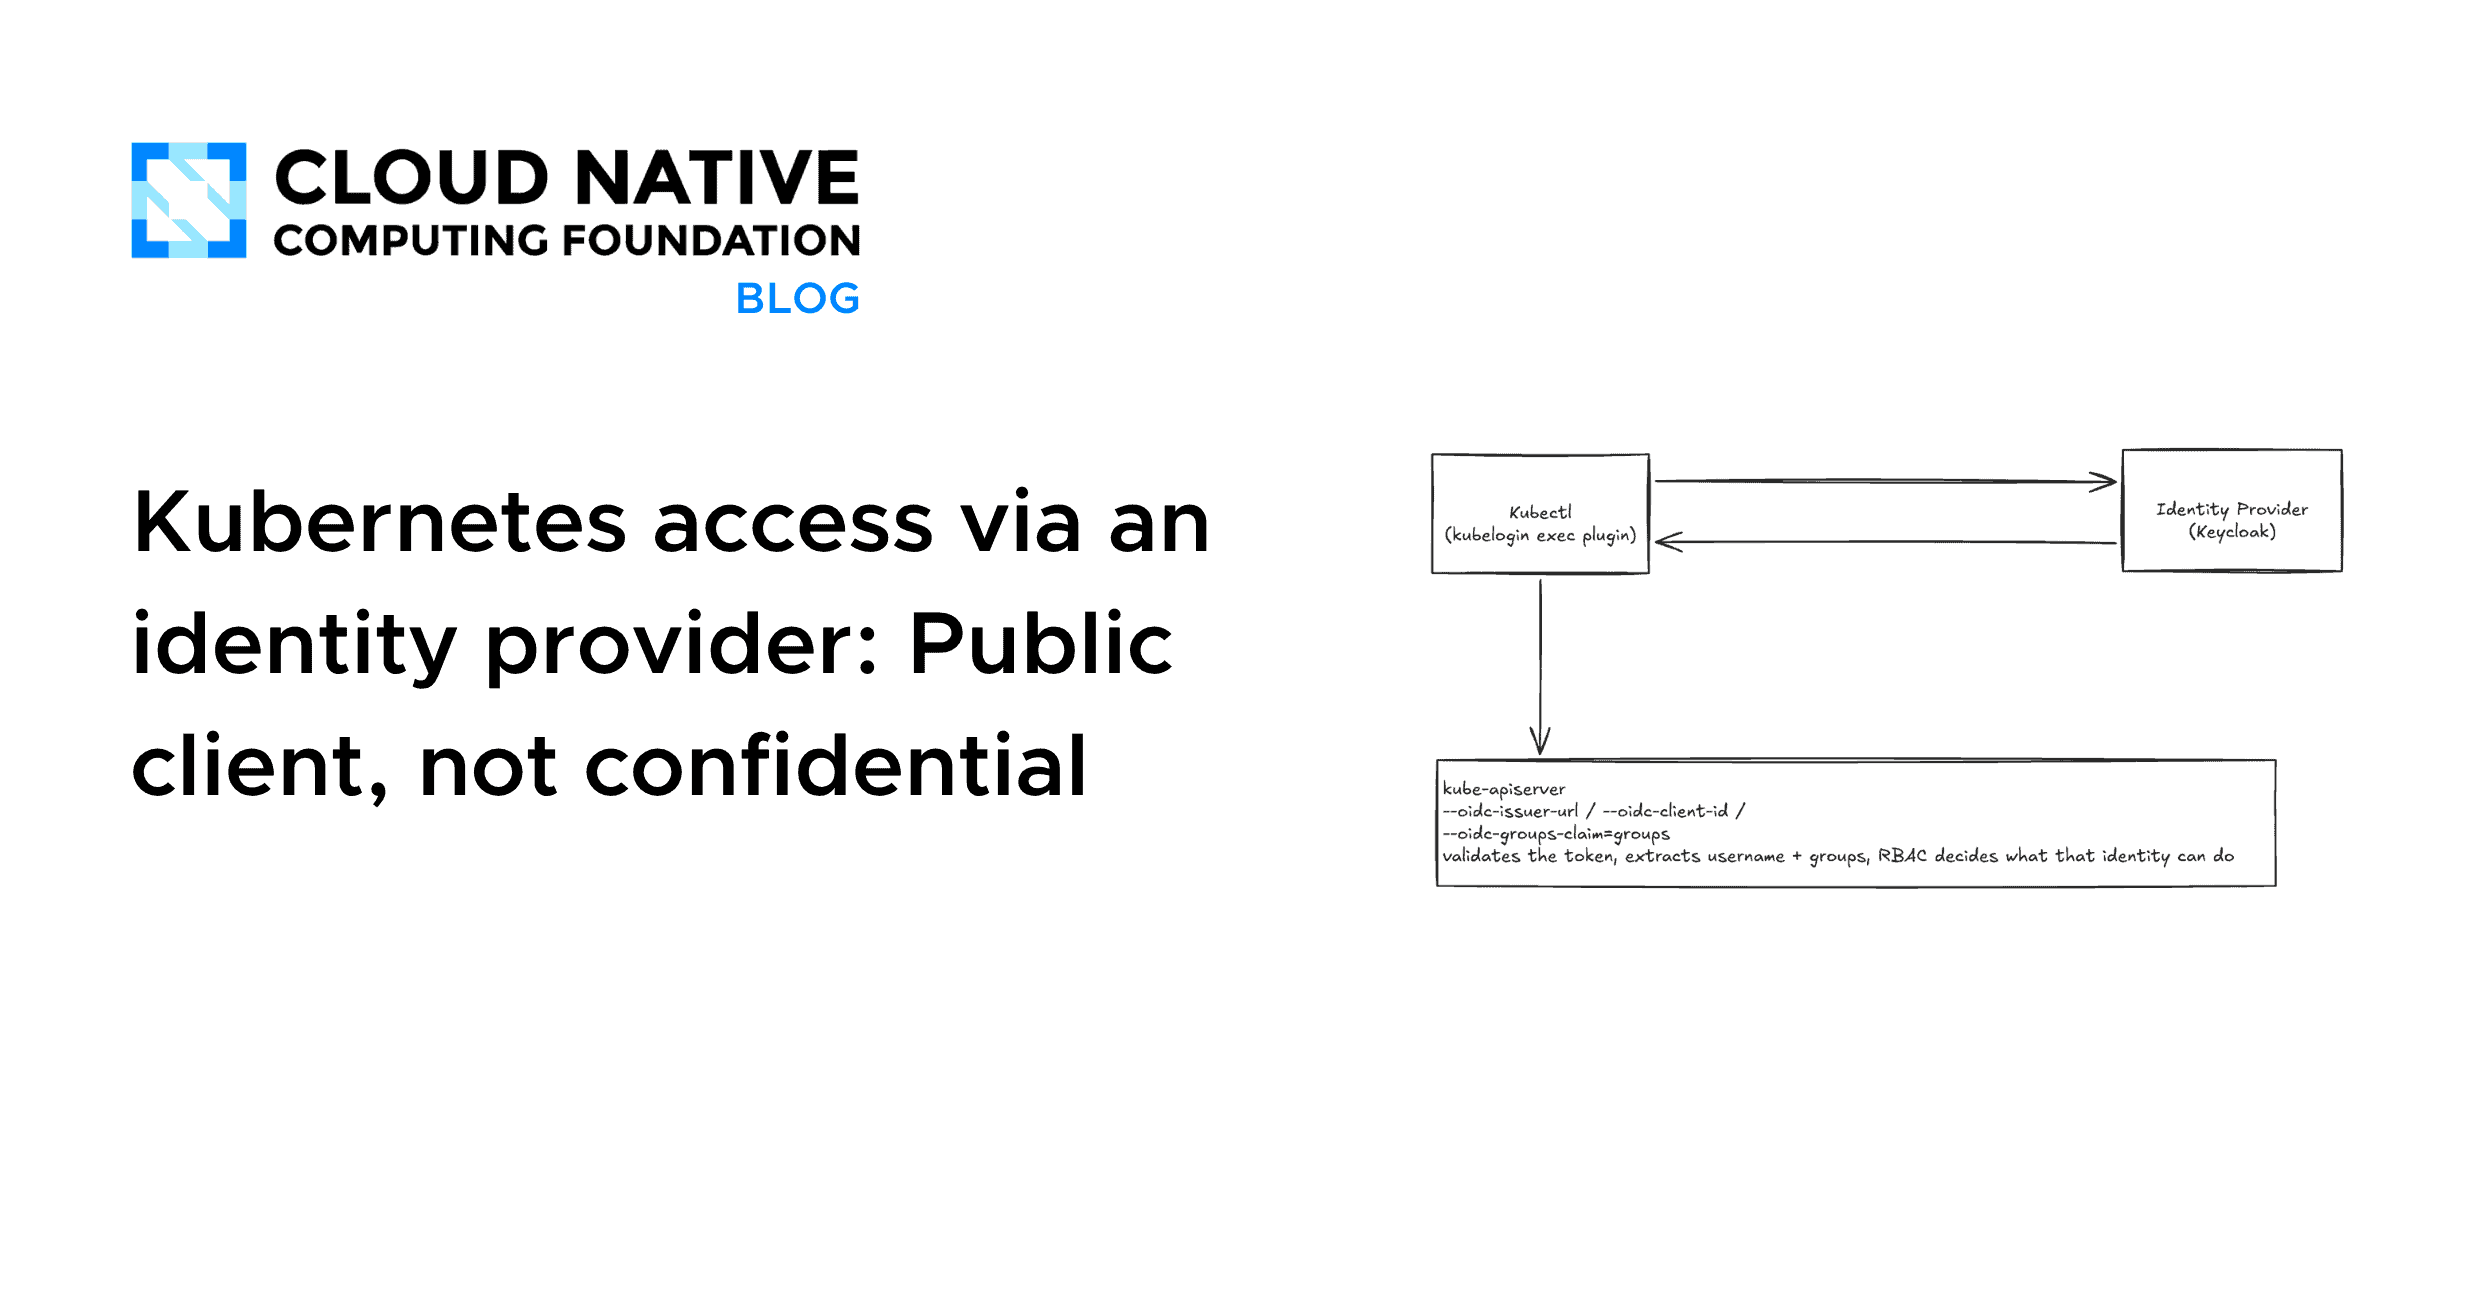
Kubernetes access via an identity provider: Public client, not confidential
Access control belongs on the same day-zero checklist as networking and storage. On most on-prem clusters, it never makes the list.
 BlogsRunning a production-ready Raspbery Pi Kubernetes cluster at homecncf.io
BlogsSecuring public AWS Application Load Balancer (ALB) with OpenID Connect (OIDC)cncf.io
BlogsKubernetes in 2025: are you ready for these top 5 trends and predictions?cncf.io
 BlogsDigital transformation driven by community: Kubernetes as examplecncf.io
 BlogsKubernetes hardening made easy: Running CIS Benchmarks with kube-benchcncf.io
 BlogsSecuring Kubernetes 1.33 Pods: The Impact of User Namespace Isolationcncf.io
EventsOdyssey: The Seven Monsters of PAMBrightTALK
EventsThe Identity Blind Spot: Why AI Agents Are the Access Control Gap…BrightTALK
Products & ServicesCisco Cyber VisionCisco
 ResourcesFrequently asked questionspine64.org
ResourcesFirst time setuppine64.org
ResourcesExtend partitionpine64.org
ResourcesEarly Adopter Editionpine64.org
ResourcesDevelopmentpine64.org
ResourcesDebuggingpine64.org
ResourcesDatasheets, schematics and certificationspine64.org
ResourcesDeveloper Editionpine64.org
ResourcesDebuggingpine64.org
ResourcesConnecting a MIPI-DSI displaypine64.org
Products & ServicesRadxa MagCase 1082radxa.com