
The technical complexities of decoupled authorization
Member post originally published on the Cerbos blog by James Walker Decoupling authorization from your main application code makes authorization more scalable, easier to maintain, and simpler to integrate with your components.
 runc container breakout vulnerabilities: A technical overviewCncf
Added flexibility and better performance are driving new use cases for WebAssemblyCncf
The importance of secrets detection and redaction within the SLSA frameworkCncf
Cloud Native GlossaryCncf
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 How to write technical documentation that developers actually useMintlify
 Launch Week III Day 3: Web Editor BranchingMintlify
 Should you build or buy an API documentation tool?Mintlify
 Flux Multilingual Technical Deep Dive: Multilingual Speech-to-Text Without the Routing MessDeepgram
 Deepgram integrates speech-to-text with UniSpeech (UniMRCP)Deepgram
 Stop Technical Debt Before It Damages Your CompanyThenewstack
 Understanding React Server ComponentsVercel
 Accent Detection AI: How It Works & When Developers Need ItDeepgram
 CNCF 2025 Community AwardsCncf
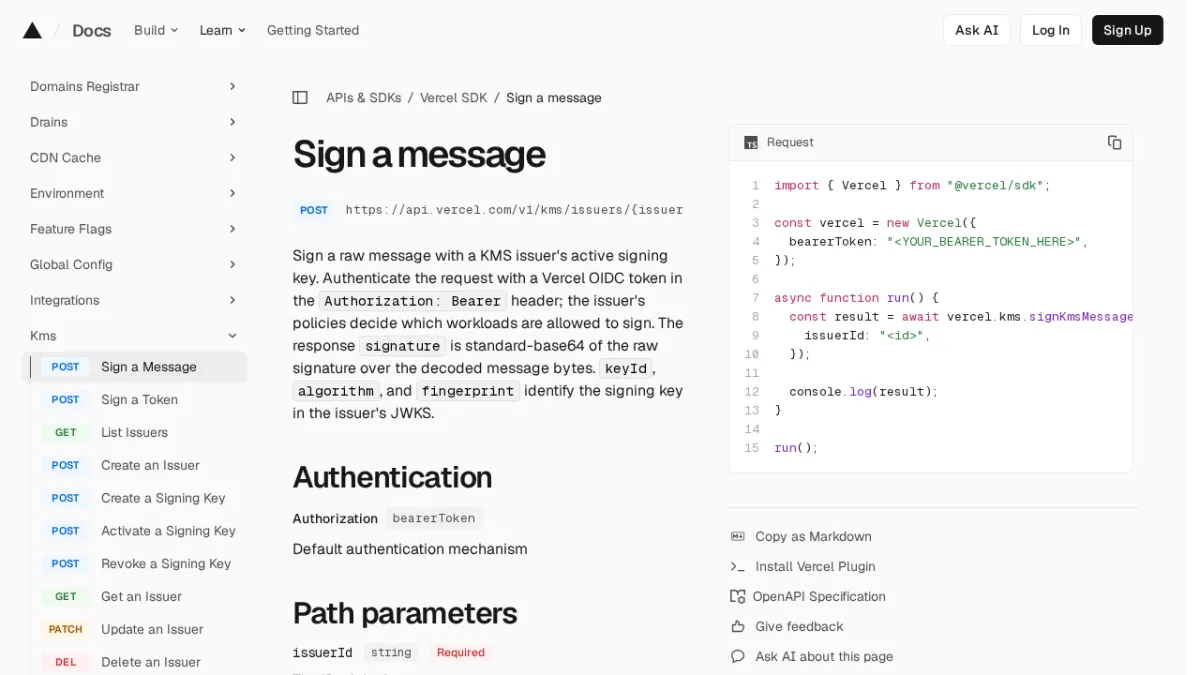 Sign a message | Vercel SDKVercel
 What Is Technical Documentation Software?Mintlify
 7 best technical search APIs for AI agents in 2026Mintlify
