
Abusing supply chains: How poisoned models, data, and third-party libraries compromise AI systems
From initial access to defense evasion, learn about common tactics attackers use to target AI artifacts in supply chains.
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 10 best AI observability tools for monitoring and evaluating agents in 2026Mintlify
 State of Speech: Our New Data Report Reveals ASR’s Untapped Potential - Deepgram Blog ⚡️Deepgram
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 The Most Important Work in AI Training Is Also the Most Overlooked - Deepgram Blog ⚡️Deepgram
 New Spanish and Turkish Language Models and Updated General Models - Deepgram Blog ⚡️Deepgram
 Data Ingestion: 6 Ways to Speed Up Your ApplicationRedis
 How a marketing agency increased client conversions 35% with Zapier CanvasZapier
 AI frameworks: Definition, types, and how to chooseZapier
 5 ways to automate Browse AIZapier
 How to connect Google Sheets to NotionZapier
 Pancakes Are Delicious and Data Centers Are for Free StuffThenewstack
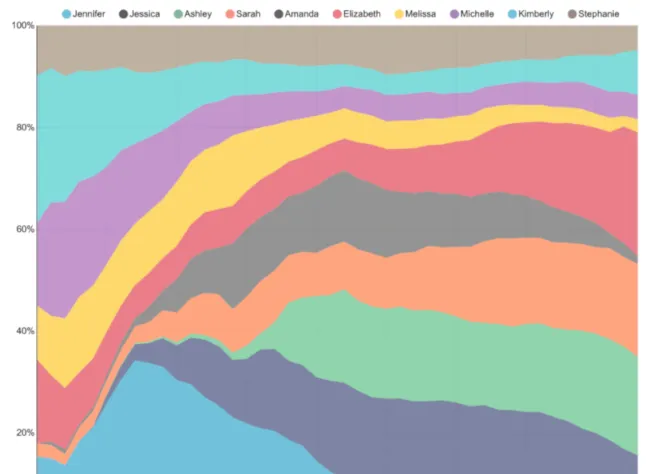 Explore and Visualize Data the Apache Superset WayThenewstack
 Cloud Systems: Deploying to Amazon ECSPulumi
