
Blogs
How to detect HTTP/2 abuse in Apache web server logs
Understand how HTTP/2 stream reset attacks exploit RST_STREAM to crash Apache workers or cause DoS.
 Mintlify Alternatives: What to Consider (and Why There's No True Substitute)Mintlify
 Calling Your Video Game With Your Phone: Part 1Deepgram
 5 ways to automate Browse AIZapier
 Grafana Is Not Worried About AWS CommercializationThenewstack
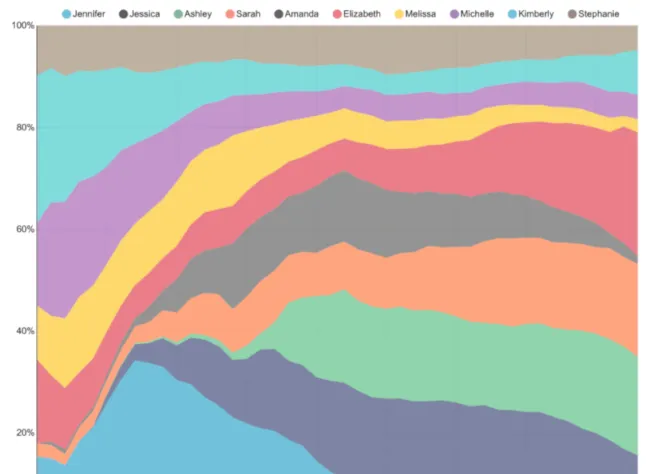 Explore and Visualize Data the Apache Superset WayThenewstack
 Real Go Projects: SmartTwitter and web.go - The Go Programming LanguageGo
 The failed promise of Web ComponentsCss Tricks
 Server-Side React RenderingCss Tricks
 Building a Remote MCP Server: OAuth, Tool Design & Lessons from 4,000+ AI Queries | MotherDuckMotherduck
 Capturing Logs in Docker DesktopDocker
 Using Web AnalyticsVercel
 Lies, damn lies, and benchmarksDeepgram
 Detect Non-Inclusive Language with Retext and Node.js - Deepgram Blog ⚡️Deepgram
 Configuration and settingsOpentelemetry
