
Key learnings from the State of DevSecOps study
We highlight the key takeaways from our 2024 State of DevSecOps study and how Datadog can help.
 State of Speech: Our New Data Report Reveals ASR’s Untapped Potential - Deepgram Blog ⚡️Deepgram
 NoSQLNow! 2014 Case Study: Bleacher Report on Redis LabsRedis
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Three Key Design Considerations for an Event-Driven ArchitectureThenewstack
 Svelte for the Experienced React DevCss Tricks
 Get assistant conversations - MintlifyMintlify
 Off-The-Shelf Hacker: Adding MQTT and Cron to the Lawn Sprinkler ProjectThenewstack
 Memory snapshots: Checkpoint/restore for sub-second startupModal
 State of DevSecOpsDatadoghq
 State of Cloud SecurityDatadoghq
 Docker State of App Dev - Dev Ex & ProductivityDocker
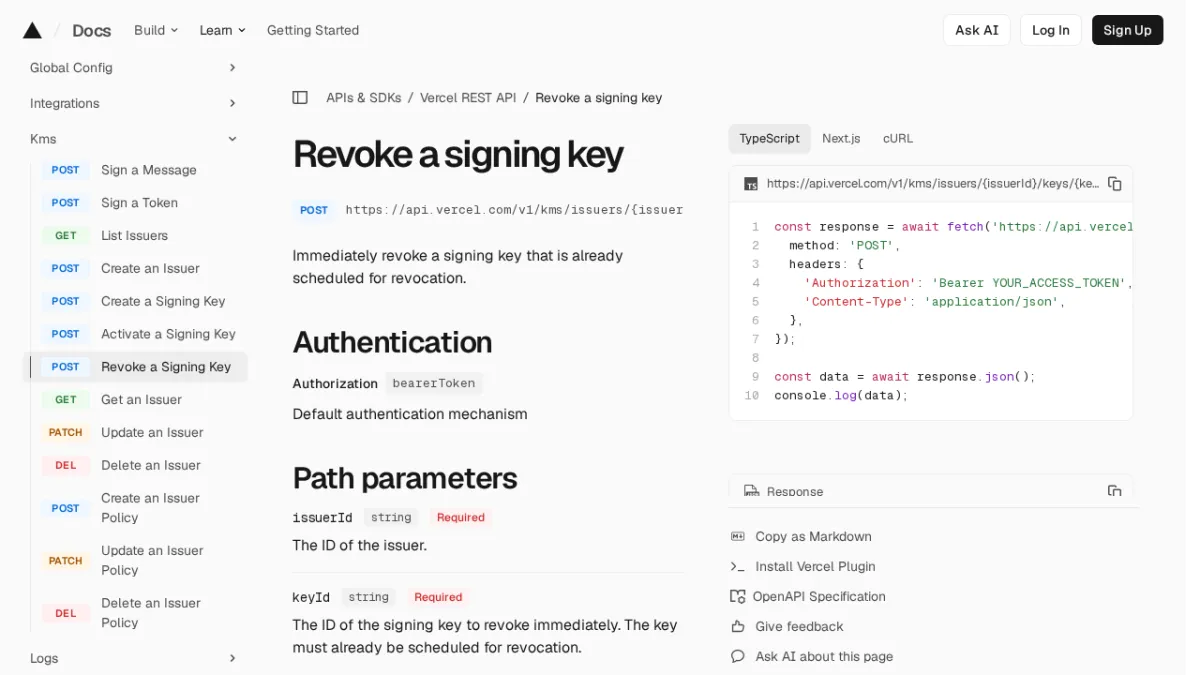 Revoke a signing key | Vercel REST APIVercel
 Should you build or buy an API documentation tool?Mintlify
 Dense Memcached with Nonvolatile MemoryThenewstack
