
New Security Measures Will Affect Older (non-OAuth 2.0) Applications
New Security Measures Will Affect Older (non-OAuth 2.0) Applications - Google Developers Blog New Security Measures Will Affect Older (non-OAuth 2.0) Applications APRIL 23, 2014 Share Facebook Twitter Linked In Mail By Antonio Fuentes, Google Identity Team There is nothing more important than making sure our users and their information stay safe online.
 Reminder to migrate to OAuth 2.0 or OpenID Connectdevelopers.googleblog.com
Smaller Fonts with WOFF 2.0 and unicode-rangedevelopers.googleblog.com
 1,000 Chrome Experiments and counting...developers.googleblog.com
 Introducing gRPC, a new open source HTTP/2 RPC Frameworkdevelopers.googleblog.com
 LiteRT.js, Google's high performance Web AI Inferencedevelopers.googleblog.com
 Google Summer of Code now open for student applicationsdevelopers.googleblog.com
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 How Argo CD and OpenShift Enable GitOps for DevelopersThenewstack
 Intel Unveils Next Generation Neuromorphic Computing ChipThenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 CSS Hell | CSS-TricksCss Tricks
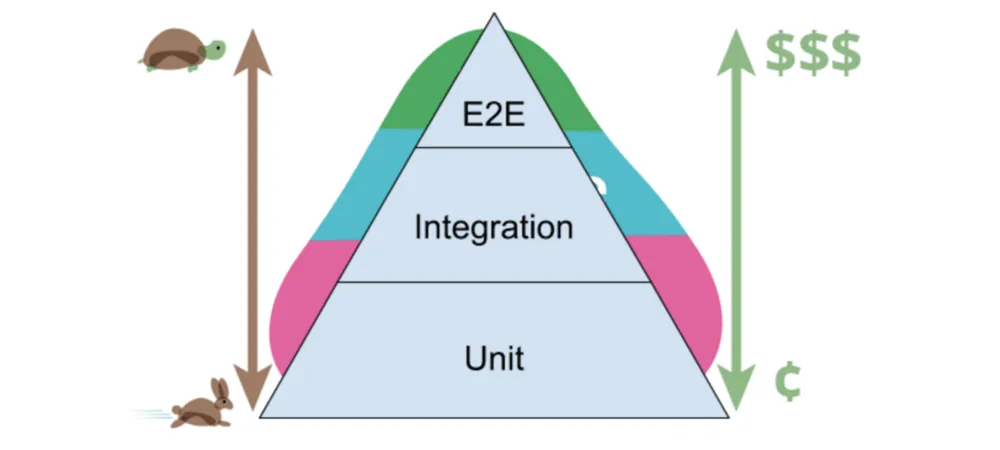 Develop, Preview, TestCss Tricks
 Building a Remote MCP Server: OAuth, Tool Design & Lessons from 4,000+ AI Queries | MotherDuckMotherduck
 KAUST and Cerebras Named Gordon Bell Award Finalist for Solving Multi-Dimensional SeismicCerebras
