
0-100 mph: Boosting App Security
0-100 mph: Boosting App Security How to accelerate your WAF visibility from 0 to 100 MPH In a drag race, how quickly you get off the line sets the tone for the race.
 Best DDoS Mitigation Providers - 2025/2026Fastly
Healthcare Under DDoS Attack: SolutionsFastly
HTTP Vary Header: Best PracticesFastly
 Next-Gen WAF for HAProxy 1.1.5 | Fastly DocumentationFastly
Fixed action for cache settings | Fastly DocumentationFastly
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 Trained on 100,000+ Voices: Deepgram Unveils Next-Gen Speaker Diarization and Language DetectionDeepgram
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 WooCommerce: App spotlightZapier
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 The App Engine SDK and workspaces (GOPATH) - The Go Programming LanguageGo
Go on App Engine: tools, tests, and concurrency - The Go Programming LanguageGo
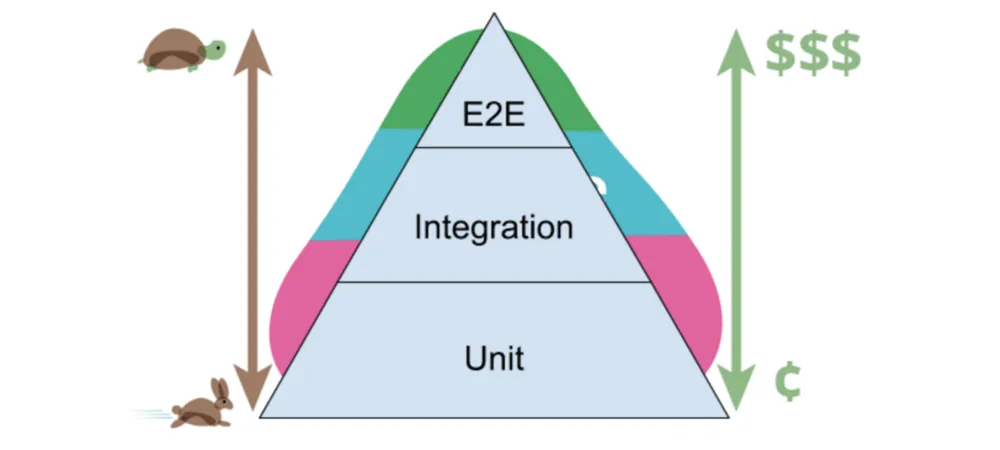 Develop, Preview, TestCss Tricks
 Some Things You Oughta Know When Working with Viewport UnitsCss Tricks
