
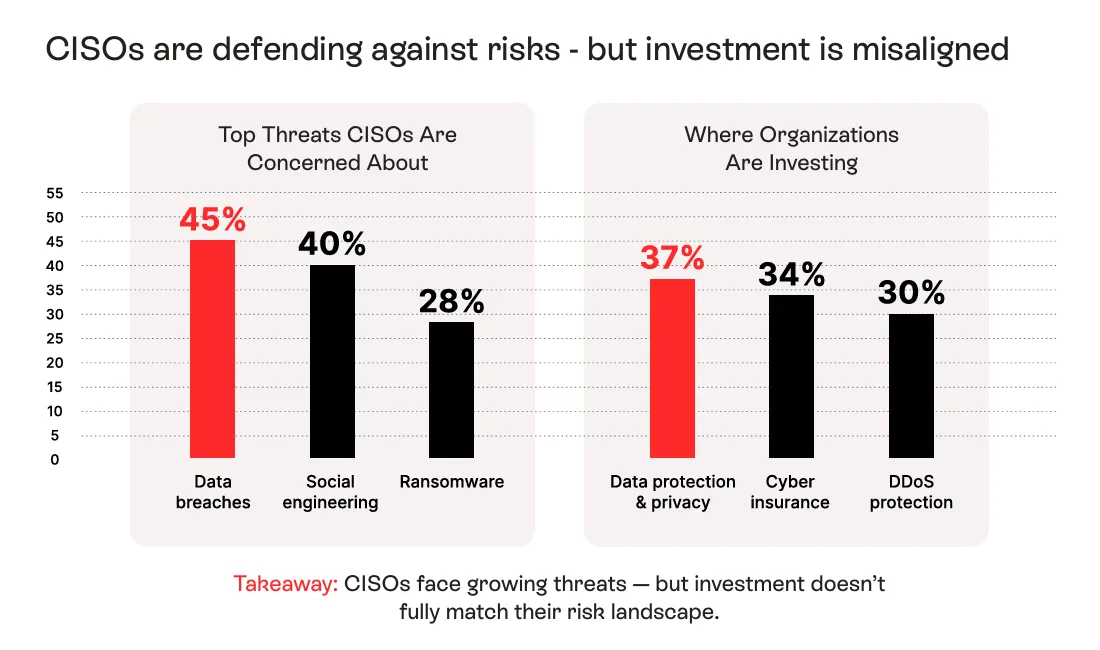
The CISO has always been accountable for incidents, but accountability has increased without giving CISOs more control. The role has moved closer to the center of the business, with CISOs more involved in incident response, exposed to board-level scrutiny, and tied to regulatory outcomes. However, a seat at the table doesn't mean control.
