
Command Injection CVE-2021-25296: A Deep Dive
A command injection vulnerability arises when unsanitized user-controlled input is used in a function that executes operating system commands.
 Best DDoS Mitigation Providers - 2025/2026Fastly
Healthcare Under DDoS Attack: SolutionsFastly
HTTP Vary Header: Best PracticesFastly
 Next-Gen WAF for HAProxy 1.1.5 | Fastly DocumentationFastly
Fixed action for cache settings | Fastly DocumentationFastly
 Automate Audio Transcription with Zapier + DeepgramDeepgram
 CLI ReferenceModal
 vercel flagsVercel
 From Hawking to Siri: The Evolution of Speech SynthesisDeepgram
 What's new at Zapier: December 2021Zapier
 Breakdown: The Kubernetes-Run AI Video Generation Pipeline for NIUS.TVThenewstack
 Neal.fun | CSS-TricksCss Tricks
 Small Data SF 2025: the Recap!Motherduck
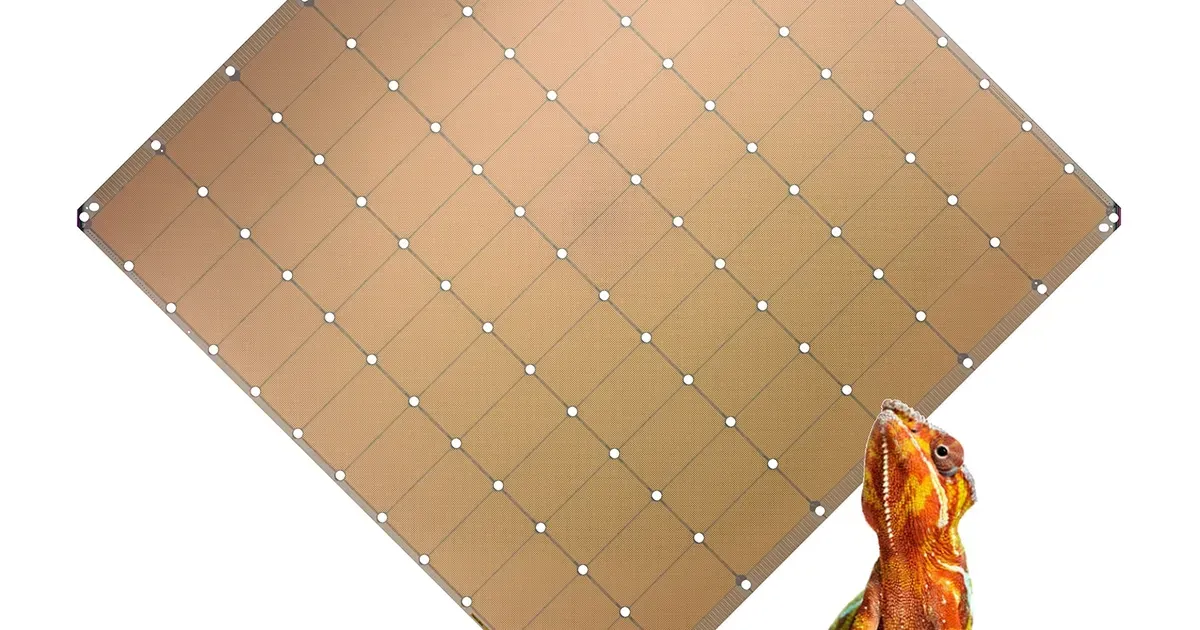 Cerebras Architecture Deep Dive: First Look Inside the HW/SW Co-Design for Deep Learning [Updated]Cerebras
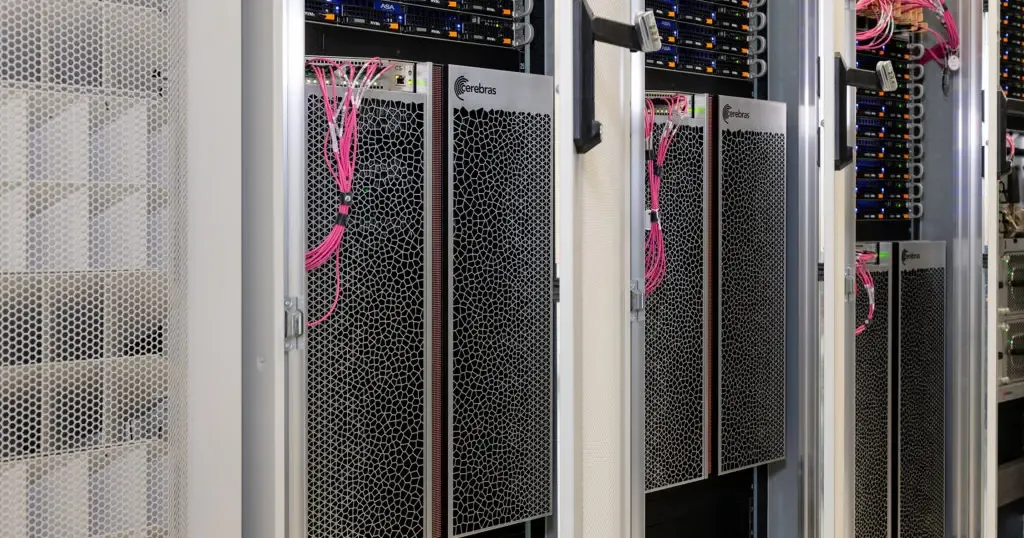 Cirrascale Cloud Services® and Cerebras Systems Announce Availability of Cerebras Cloud @ CirrascaleCerebras
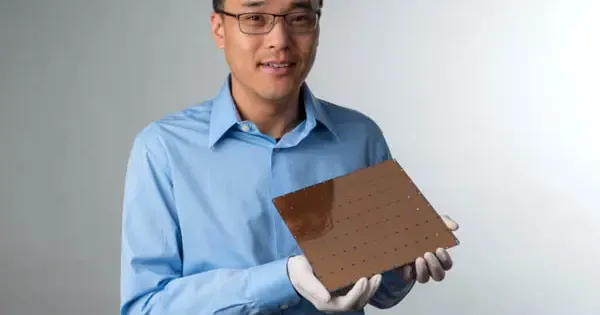 Announcing the Cerebras Architecture for Extreme-Scale AI - CerebrasCerebras
 vercel projectVercel
 How to Get a Job in Deep Learning - Deepgram Blog ⚡️Deepgram
 Flux Multilingual Technical Deep Dive: Multilingual Speech-to-Text Without the Routing MessDeepgram
