
Knowing what not to attack
Most talk about offensive security agents is about power. Can it find the bug? Can it chain the exploit? Can it own the box? That's the easy part. Wiring
 CVE‑2025‑49113 – Post‑Auth Remote Code Execution in Roundcube via PHP Object Deserializationoffsec.com
 When AI Becomes the Weak Link: Rethinking Supply Chain Securityoffsec.com
 CVE-2024-13059: Exploiting Path Traversal in AnythingLLM for Remote Code Executionoffsec.com
 CVE-2025-32433: Vulnerability in Erlang/OTP SSH Implementationoffsec.com
 CVE-2025-29927: Next.js Middleware Authorization Bypassoffsec.com
 CVE-2024-2928: MLflow Local File Inclusion via URI Fragment Manipulationoffsec.com
 Grafana Is Not Worried About AWS CommercializationThenewstack
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Inside the Go Playground - The Go Programming LanguageGo
 The Anatomy of shadcn/ui ComponentsVercel
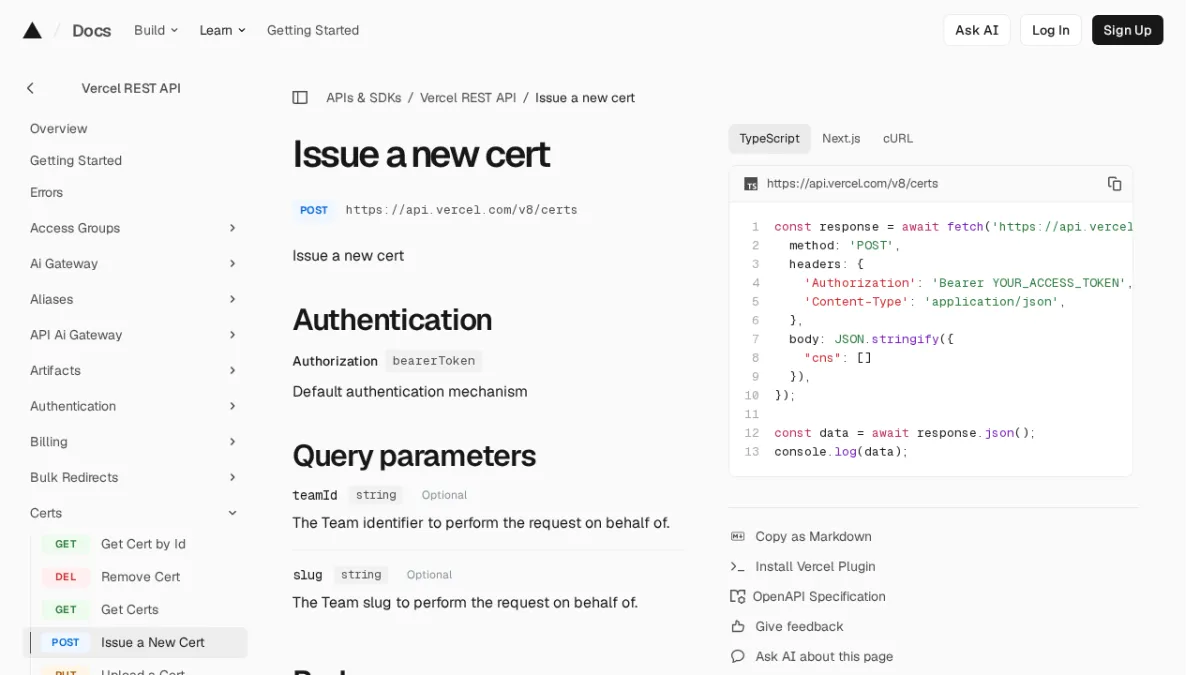 Issue a new certVercel
 Anthropic Identifies Biased Reasoning and Recklessness as Drivers of Claude’s PyPI AttackSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 Training: Hard Work Pays off for Data/AI ProsThenewstack
 Your Perfect Infrastructure May Not Be So PerfectPulumi
 Effective Go - The Go Programming LanguageGo
 Defining “View Source”Css Tricks
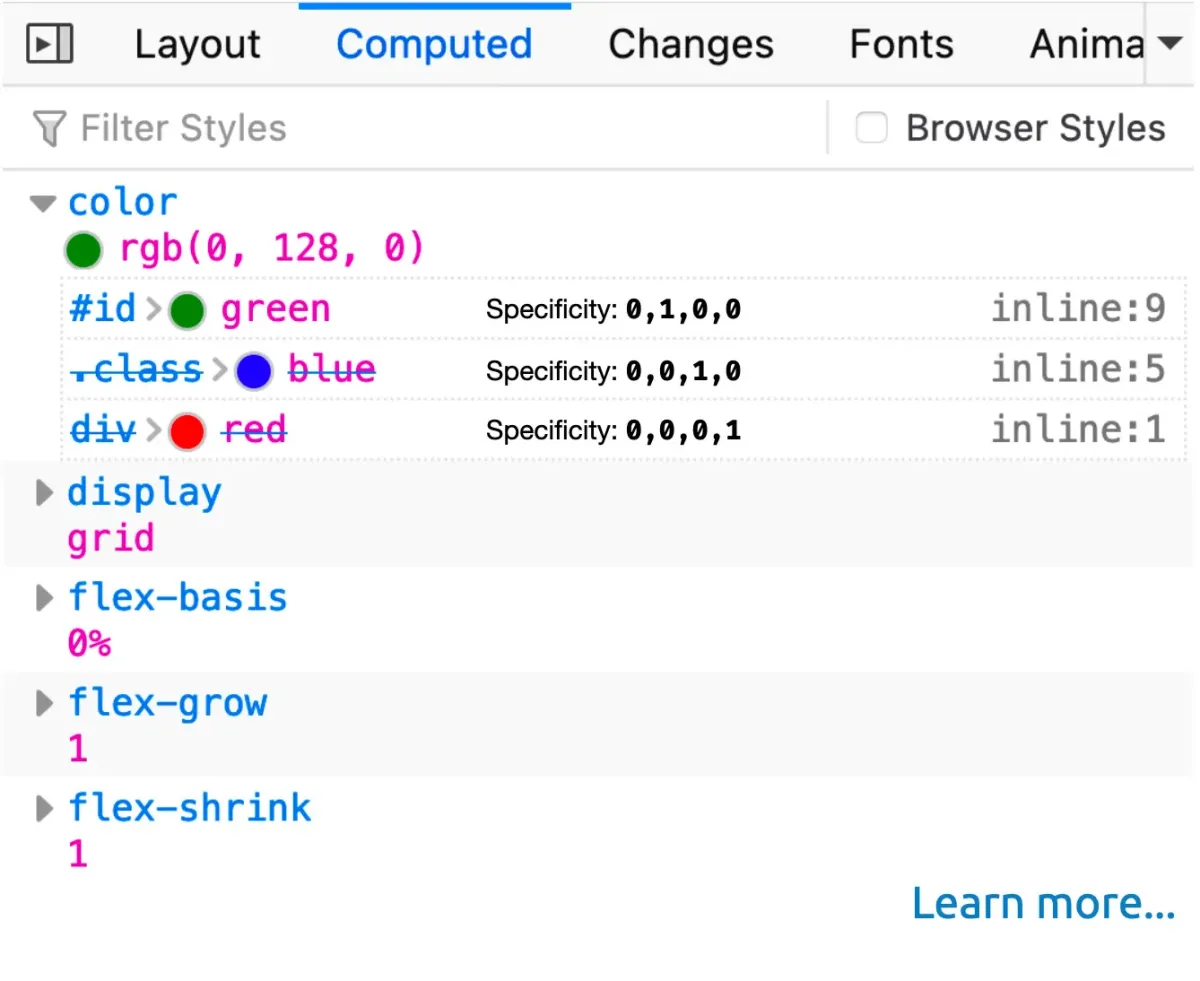 Should DevTools teach the CSS cascade?Css Tricks
 Cerebras Systems Sets Record for Largest AI Models Ever Trained on A Single Device - CerebrasCerebras
