
OpenAI introduces its Outbound Coordinated Disclosure Policy to guide how it responsibly reports vulnerabilities in third-party software—emphasizing integrity, collaboration, and proactive security at scale.
Recommended
Simplifying, stabilizing, and scaling continuous-time consistency modelsOpenai Security on the path to AGIOpenai GPT-6.1 Sol helps CodeRabbit strengthen security across complex codebasesOpenai Strengthening democratic oversight in national securityOpenai Rapidly scaling online storage to serve over 1 billion ChatGPT users (Part II)Openai Fair use benefits everyoneOpenai
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 Redis Achieves ISO 27001 Cybersecurity CertificationRedis
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 WooCommerce: App spotlightZapier
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 Scaling Organizations Should Consider Building a Website Backed by a CRM PlatformCss Tricks
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
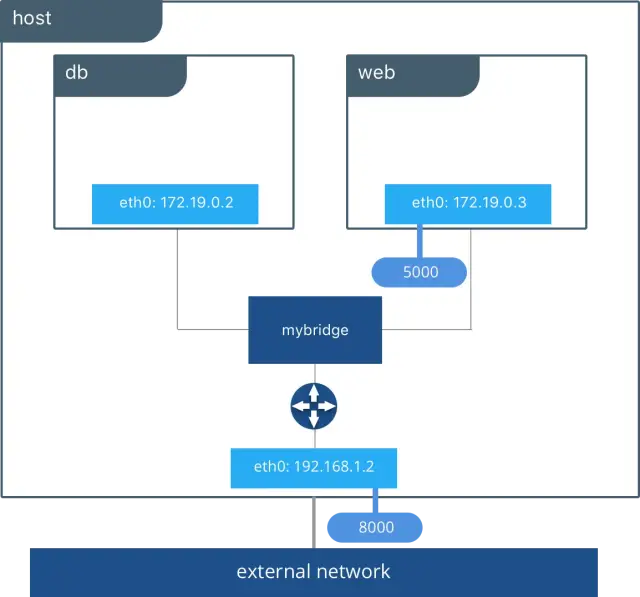 Docker Networking Drivers - Details and Use CasesDocker
 Two-factor AuthenticationVercel
