
Prompt injections are a frontier security challenge for AI systems. Learn how these attacks work and how OpenAI is advancing research, training models, and building safeguards for users.
Recommended
Security on the path to AGIOpenai GPT-6.1 Sol helps CodeRabbit strengthen security across complex codebasesOpenai Strengthening democratic oversight in national securityOpenai Credit Saison achieves 954% ROI in a ChatGPT Enterprise pilotOpenai Making it easier for websites to express AI training preferencesOpenai Community safety report and new protections for teensOpenai Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 Redis Achieves ISO 27001 Cybersecurity CertificationRedis
Let’s Play Master and Servant: Real Time Synchronization Tool for Redis MigrationRedis
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 How Hunch supercharged AI workflows with Modal SandboxesModal
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
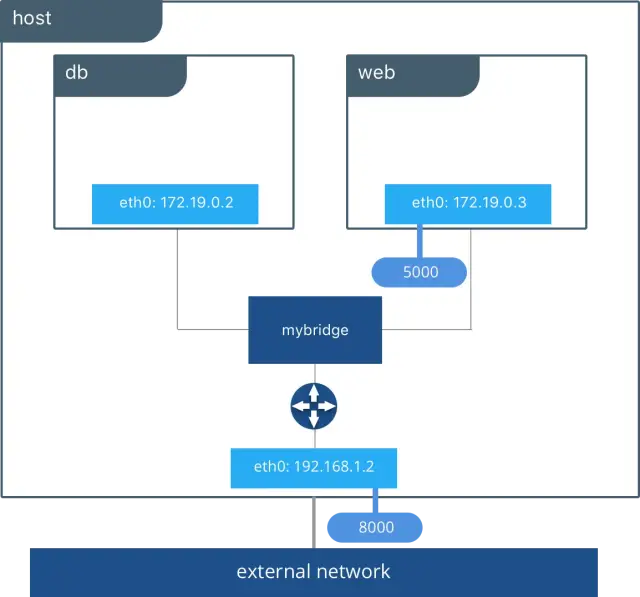 Docker Networking Drivers - Details and Use CasesDocker
 A prompt guide to get the most out of HeyGen's new Video AgentHeygen
