
Keep your secrets secure, by default
Pulumi keeps your infrastructure passwords, tokens, keys, and more secure, by default.
 AWS Serverless AnalyticsPulumi
Running AWS IAM Access Analyzer at Deployment TimePulumi
Manage Any Infrastructure with Policy as CodePulumi
Managing Kubernetes Infrastructure with .NET and PulumiPulumi
Deploy Serverless Containers on Google Cloud Run with PulumiPulumi
2019 Year at a GlancePulumi
 5 Reasons to Keep Contributing to Open-Source Projects - Deepgram Blog ⚡️Deepgram
 Integrate Jupyter Notebooks with GitHubThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Pushing Pulumi ESC Secrets into External PlatformsPulumi
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
 Facebook Subscription Groups for ContentHeygen
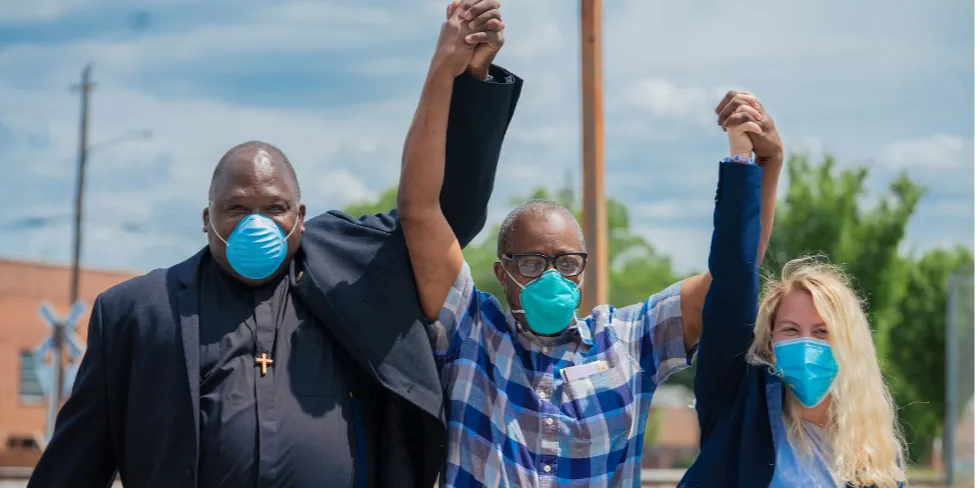 How the Georgia Innocence Project uses automation to keep all its systems runningZapier
 Linux and Cloud Native Security: AlmaLinuxThenewstack
 What is Workflow Automation?Datadoghq
 Aleph Alpha Selects Cerebras to Build Next-Gen Sovereign AI Models - CerebrasCerebras
 HTML | KotlinKotlinlang
 Protecting Secrets with DockerDocker
 DockerCon Workshops: Getting Started with Docker, AI/ML, Secure DevelopmentDocker
