
A day in the life: Supply Chain Security Researcher
This will give a glimpse into what it is like to be a Security Researcher on the Semgrep Supply Chain Security Research team!
 Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
Detect Open Source Malware Attacks with Semgrep Supply ChainSemgrep
London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Semgrep × Cursor Hooks: Making Security Reliable for AgentsSemgrep
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 How we grew Mintlify by doing things that don't scaleMintlify
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Lessons Swift Designer Chris Lattner Has Learned about LeadershipThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 Anthropic integration with Modal brings scalable compute to Claude ScienceModal
 Revolutionizing Life Science and Healthcare with Generative AI - CerebrasCerebras
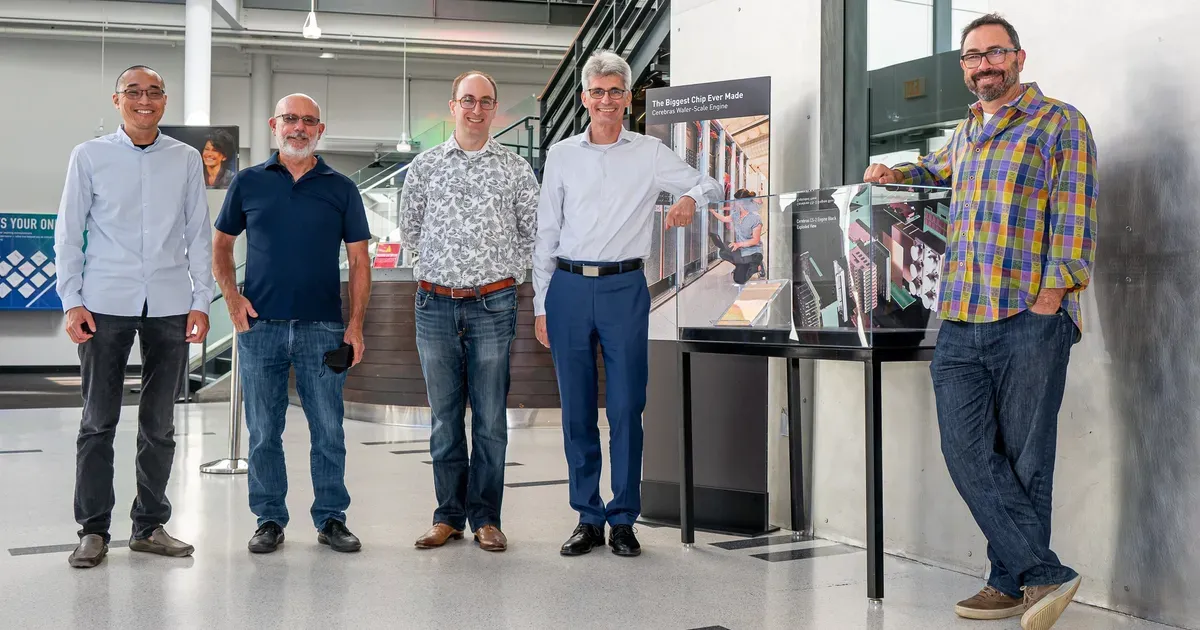 Cerebras Wafer-Scale Engine Inducted into the Computer History Museum - CerebrasCerebras
