
A deep dive into Semgrep Supply Chain
Top level goal of an App Sec supply chain program Are you an App Sec engineer? Are you trying to minimize the mass exploitability of your attack surface?
 Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
Detect Open Source Malware Attacks with Semgrep Supply ChainSemgrep
London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
 Automate Audio Transcription with Zapier + DeepgramDeepgram
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 NO_EXTERNAL_CSS_AT_IMPORTSVercel
 From Hawking to Siri: The Evolution of Speech SynthesisDeepgram
 How Mondelez Accelerates Supply Chain Training Across 150+ Global Manufacturing PlantsSynthesia
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 Supply Chain Attacks and Cloud Native: What You Need to KnowThenewstack
 Breakdown: The Kubernetes-Run AI Video Generation Pipeline for NIUS.TVThenewstack
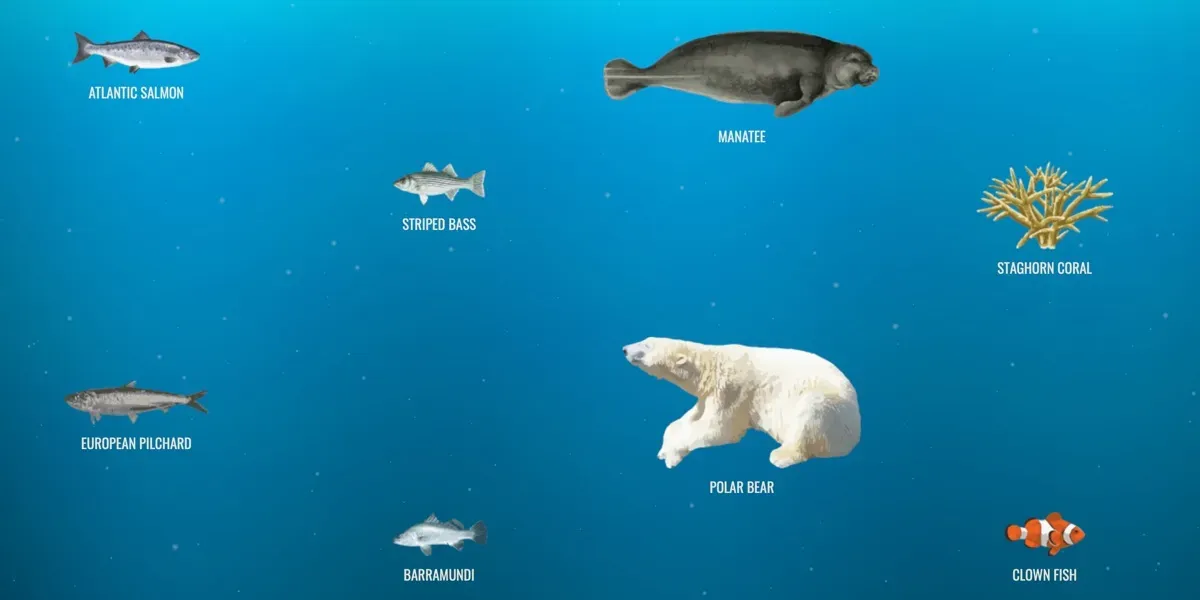 Neal.fun | CSS-TricksCss Tricks
 Small Data SF 2025: the Recap!Motherduck
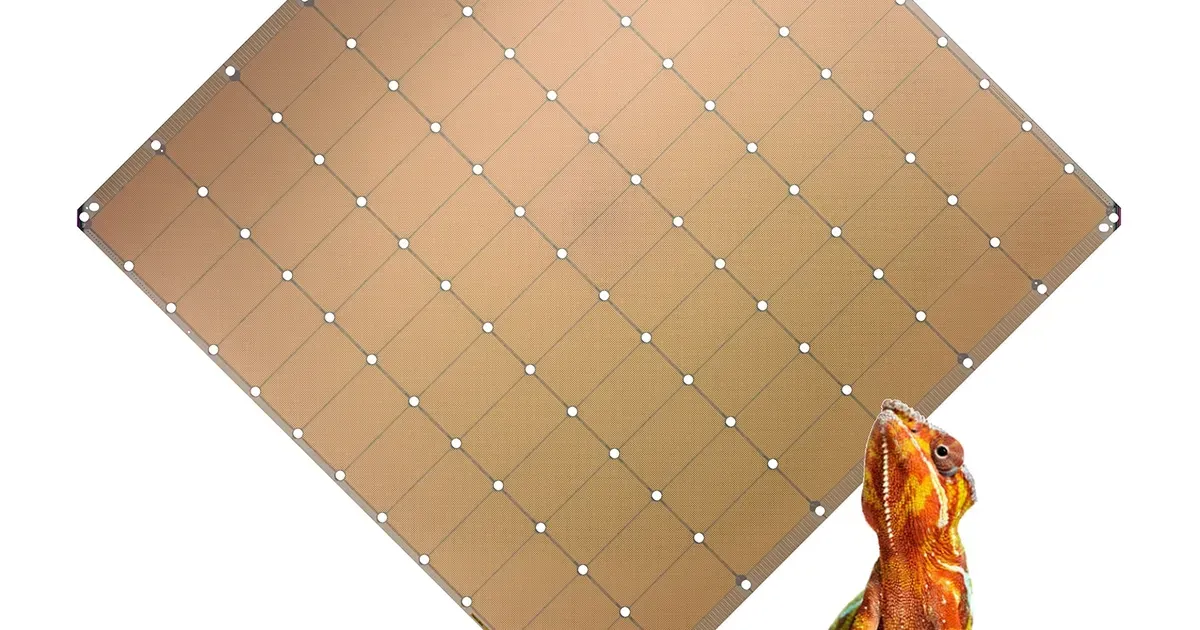 Cerebras Architecture Deep Dive: First Look Inside the HW/SW Co-Design for Deep Learning [Updated]Cerebras
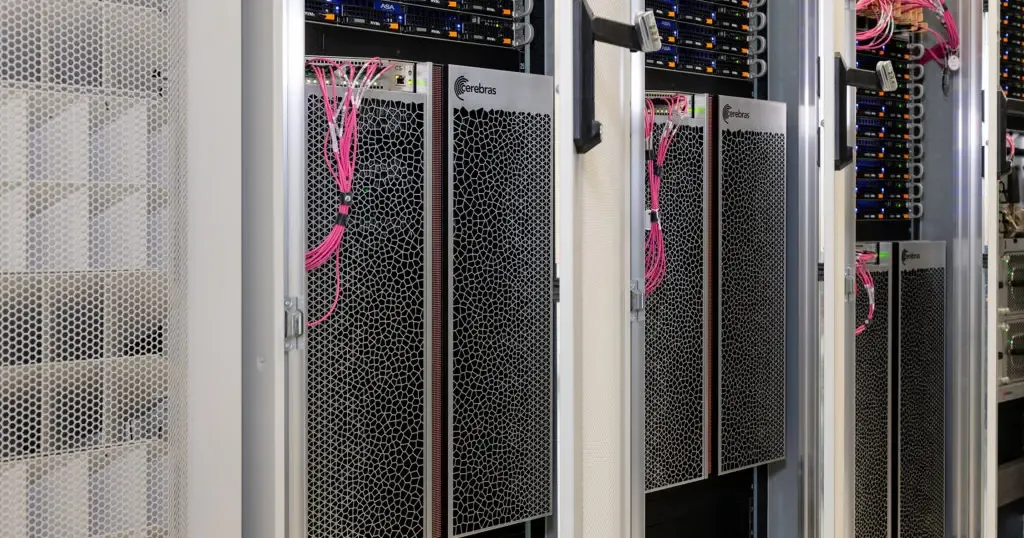 Cirrascale Cloud Services® and Cerebras Systems Announce Availability of Cerebras Cloud @ CirrascaleCerebras
 Webinar Recap: Webinar Recap: Securing the Software Supply Chain with Docker BusinessDocker
