
Expanding Semgrep Supply Chain into Dependency Intelligence and License Compliance
With Semgrep Supply Chain, you can now mitigate supply chain vulnerabilities before a CVE even drops with Dependency Search and enforce your organization's license policies on pull requests with License Compliance.
 Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
Detect Open Source Malware Attacks with Semgrep Supply ChainSemgrep
London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 The Most Important Work in AI Training Is Also the Most Overlooked - Deepgram Blog ⚡️Deepgram
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Cerebras Systems Enables GPU-Impossible™ Long Sequence Lengths Improving Accuracy in NaturalCerebras
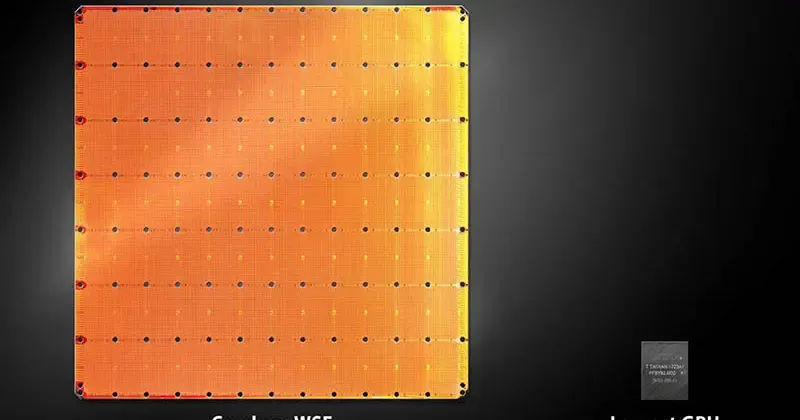 Cerebras Systems Unveils the Industry’s First Trillion Transistor Chip - CerebrasCerebras
 NO_EXTERNAL_CSS_AT_IMPORTSVercel
 How Mondelez Accelerates Supply Chain Training Across 150+ Global Manufacturing PlantsSynthesia
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Introducing Dependency Divergence GitHub ActionSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 Training: Hard Work Pays off for Data/AI ProsThenewstack
 Supply Chain Attacks and Cloud Native: What You Need to KnowThenewstack
 Announcing dependency caching for Pulumi DeploymentsPulumi
