
Fully loaded: testing vulnerable PyYAML versions
❗ tl;dr: By testing the PyYAML API across various released versions, we determined that the yaml.Loader class is unsafe in all released versions.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 From Gatekeepers to Guardrails: Automating Your PCI DSS v4.0.1 StrategySemgrep
 Supporting Kubernetes with Faster, Easier Test EnvironmentsPulumi
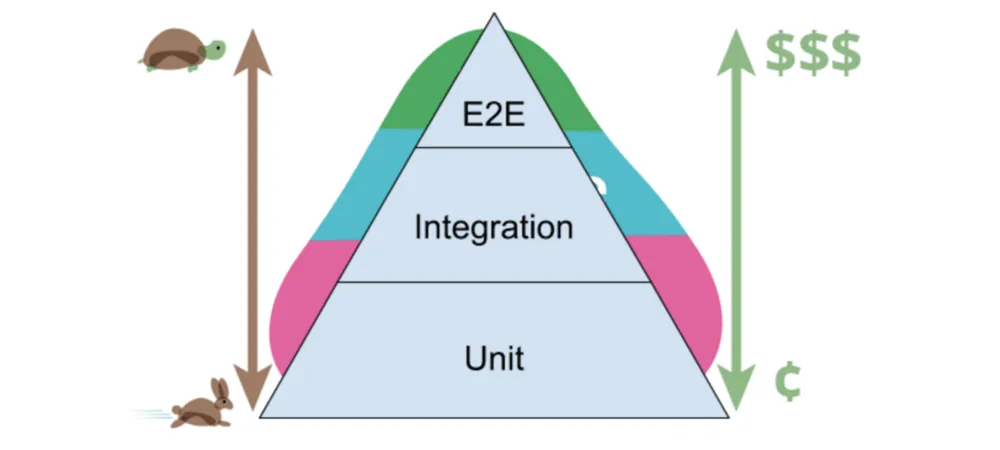 Develop, Preview, TestCss Tricks
 Voice AI for Government: Speech-to-Text for Government MissionsDeepgram
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 GlassWorm Loader Hits Open VSX via Developer Account CompromiseSocket
 Improving Pulumi’s Docker ImagesPulumi
 Vercel Data Cache: A progressive cache, integrated with Next.jsVercel
 How to Fully Delete a Git Repository Created with Init? | Better Stack CommunityBetterstack
 PolinRider Spreads Through Compromised GitHub Accounts and PackagistSocket
 Lessons Learned from a Year of Testing the Web PlatformCss Tricks
 Fetch directive - GlossaryDeveloper Mozilla
 Markdown export - MintlifyMintlify
 7 best MCP servers for Claude Code in 2026Mintlify
 AI in Finance: Money Making MachinesDeepgram
