
Miasma v3 Hits AsyncAPI: Is NPM Hardening Working?
Miasma v3 compromised 4 AsyncAPI npm packages using a load-time payload with worm capabilities deliberately disabled.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 Lessons Swift Designer Chris Lattner Has Learned about LeadershipThenewstack
 Data connections - FeaturesJetbrains
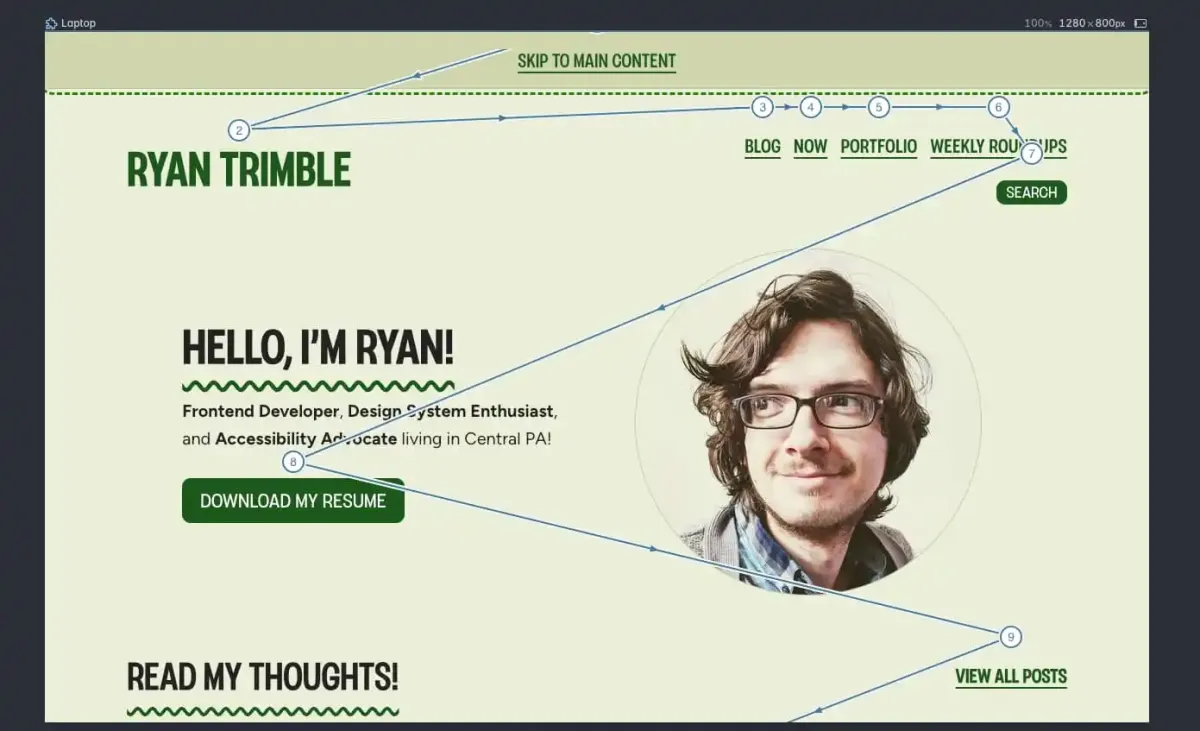 Clever Polypane Debugging Features I'm LovingCss Tricks
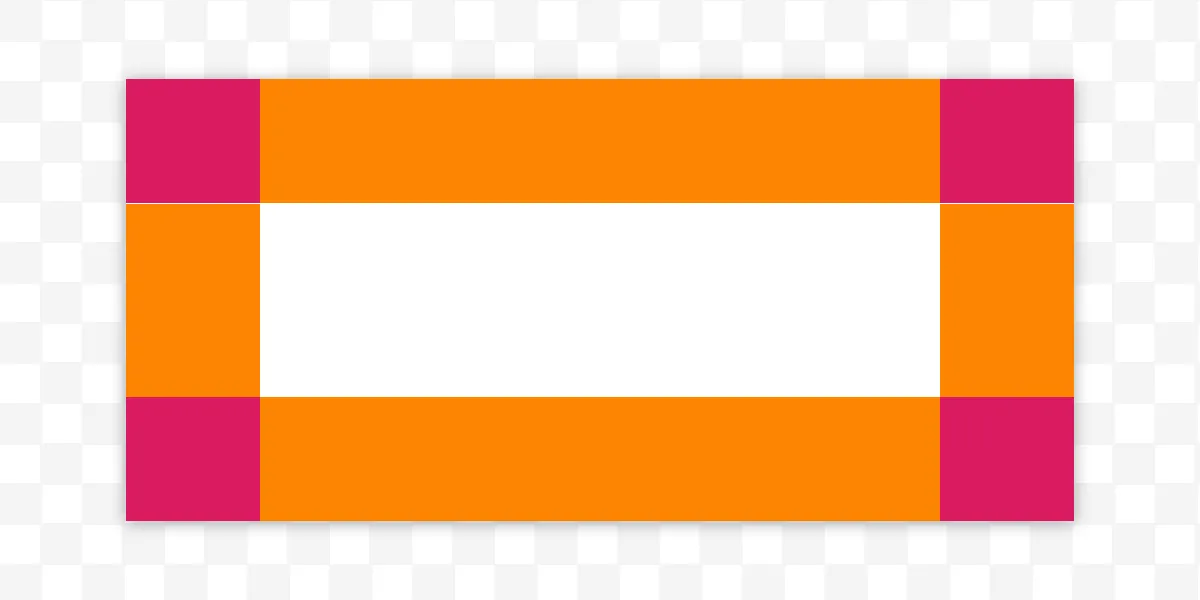 Some Things You Oughta Know When Working with Viewport UnitsCss Tricks
 MotherDuck Builder Office Hours - July 21Motherduck
 AsyncAPI setup - MintlifyMintlify
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 Happy Birthday, Shai-HuludSocket
 GlassWorm Loader Hits Open VSX via Developer Account CompromiseSocket
 Insurance Social Media Marketing: A Practical GuideHeygen
 Learning in the Flow of Work: How to Design for ImpactSynthesia
 How to Protect Your Projects from the Risks of Deprecated npm PackagesSocket
 When "Everything" Becomes Too Much: The npm Package Chaos of 2024Socket
