
New Sandbox Escape Affecting Popular nodejs Sandbox library vm2
Popular Node.js sandboxing library vm2 has just announced a critical vulnerability in their library which allows attackers to bypass their promise sanitization and execute arbitrary code, escaping the sandbox.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 From Gatekeepers to Guardrails: Automating Your PCI DSS v4.0.1 StrategySemgrep
 Video: Building a Live Transcription Badge With Deepgram - Deepgram Blog ⚡️Deepgram
 Automate Audio Transcription with Zapier + DeepgramDeepgram
 Grafana Is Not Worried About AWS CommercializationThenewstack
 AWS Enterprise Container Management with PulumiPulumi
 Unpacking sandbox startup latency: why started ≠ readyModal
 Sidecars: A low-latency trust boundary for SandboxesModal
 Butter is joining ModalModal
 Product updates: Rollbacks, batching, sandbox tunnels & moreModal
 Product updates: Modal Notebooks, sandbox idle timeouts, and moreModal
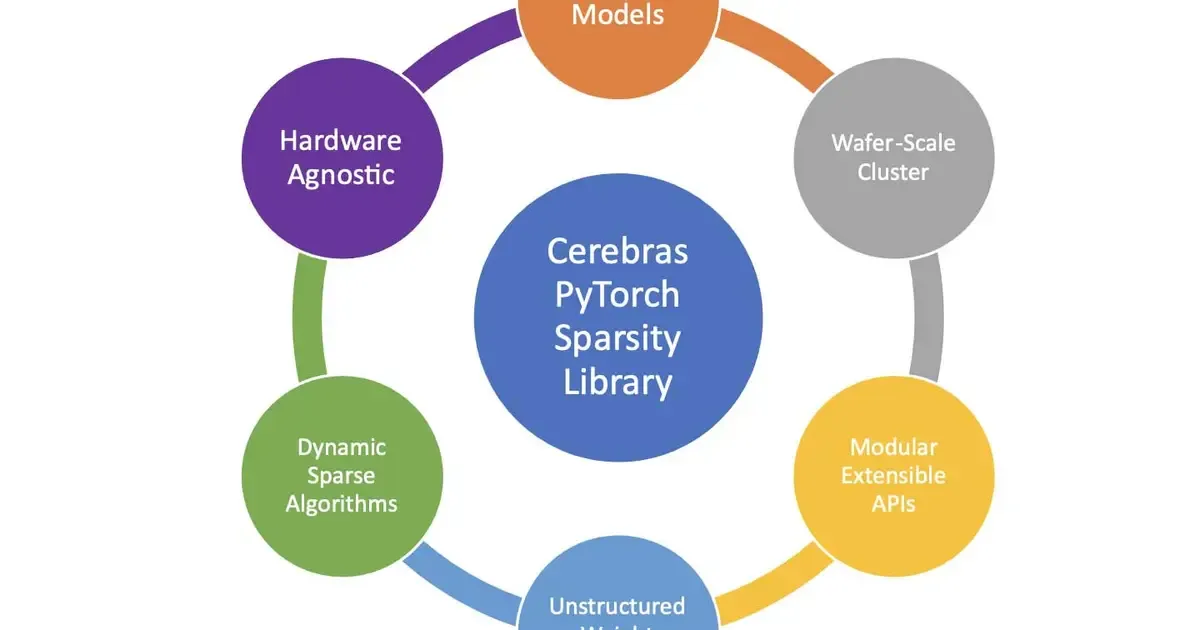 Sparsity Made EasyCerebras
 Financial Education Video Library: Where to StartHeygen
 Partnering with Shutterstock to accelerate our AI research effortsSynthesia
 amoCRM: App of the dayZapier
 Popular npm Packages in the keyv and Cacheable Namespaces Compromised in Active Supply Chain AttackSocket
