
Should random() be banned?
Thought experiment: should the use of non-cryptographically secure random() be flagged to developers (examples: Bandit and gosec)?
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 From Gatekeepers to Guardrails: Automating Your PCI DSS v4.0.1 StrategySemgrep
 The Language of LGBTQ Inclusion and Allyship - Deepgram Blog ⚡️Deepgram
 5 Reasons to Keep Contributing to Open-Source Projects - Deepgram Blog ⚡️Deepgram
 Server-Side React RenderingCss Tricks
 Scaling Organizations Should Consider Building a Website Backed by a CRM PlatformCss Tricks
 6 tips every developer should know when using Cursor and Windsurf AIMintlify
 How the AI Business World Actually Works: A Startup’s WarDeepgram
 Why you should ditch spreadsheets for TablesZapier
 Supply Chain Attacks and Cloud Native: What You Need to KnowThenewstack
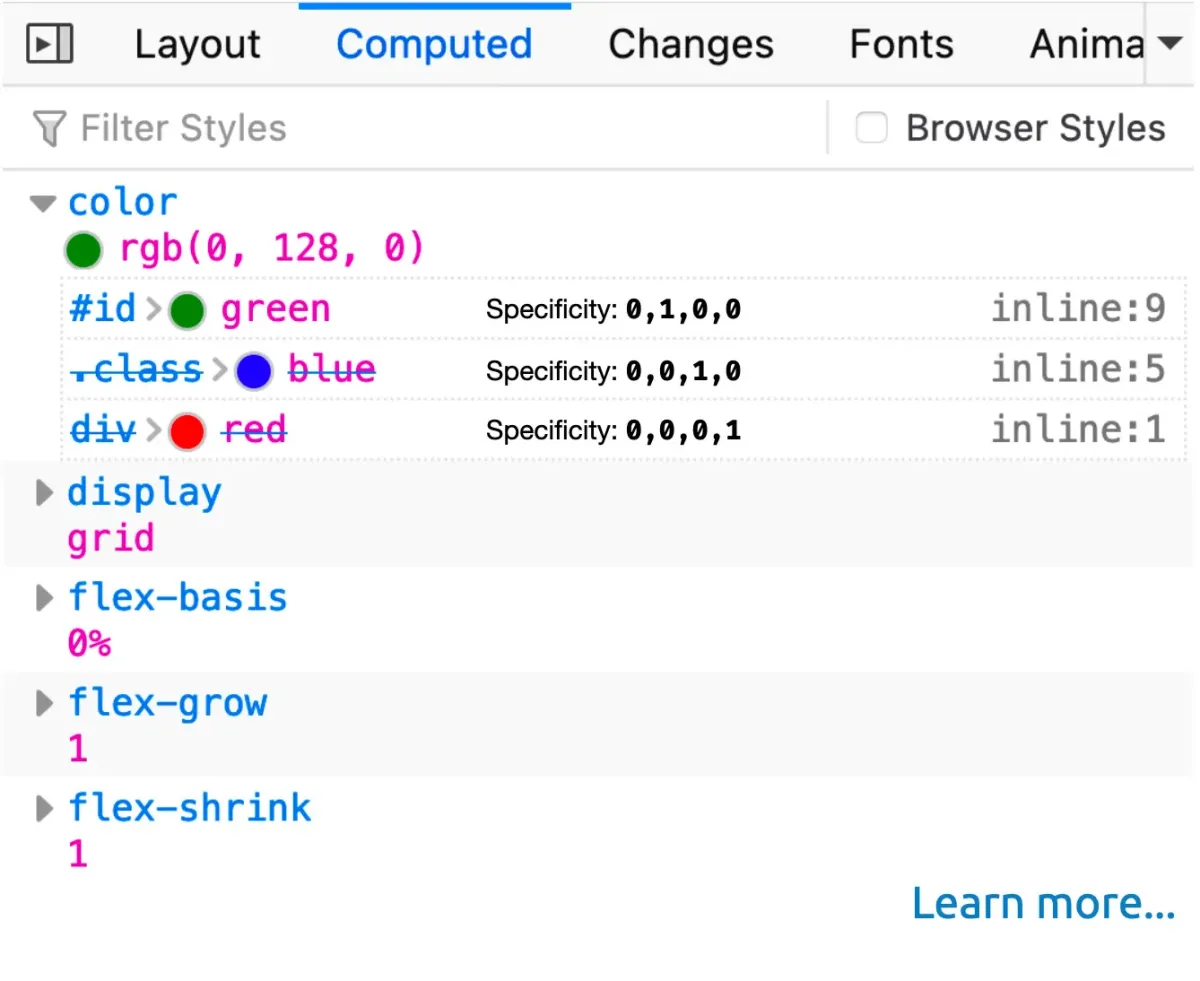 Should DevTools teach the CSS cascade?Css Tricks
 Should you build or buy an API documentation tool?Mintlify
 What Observability Should Do for Your OrganizationThenewstack
 Markdown vs MDX: which should you use for documentation?Mintlify
 Be Efficient, Not ProductiveZapier
 6 ways to automate Facebook custom audiencesZapier
