
Surprising subtleties of Docker permissions
The fundamental building block of our analysis platform is an analyzer. Since the static analysis world works in many different languages and can require many different libraries, each analyzer is its own Docker image, and the Dockerfile is provided by the analysis author.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 From Gatekeepers to Guardrails: Automating Your PCI DSS v4.0.1 StrategySemgrep
 Flockport: Time to Start All Over Again and Return to LXC ContainersThenewstack
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 Introducing New Slimmer Docker ImagesPulumi
 Docker Captain Take 5Docker
 Docker Community All Hands RecapDocker
 Docker Desktop 4.23: Updates to Docker Init, New Configuration Integrity Check, Quick SearchDocker
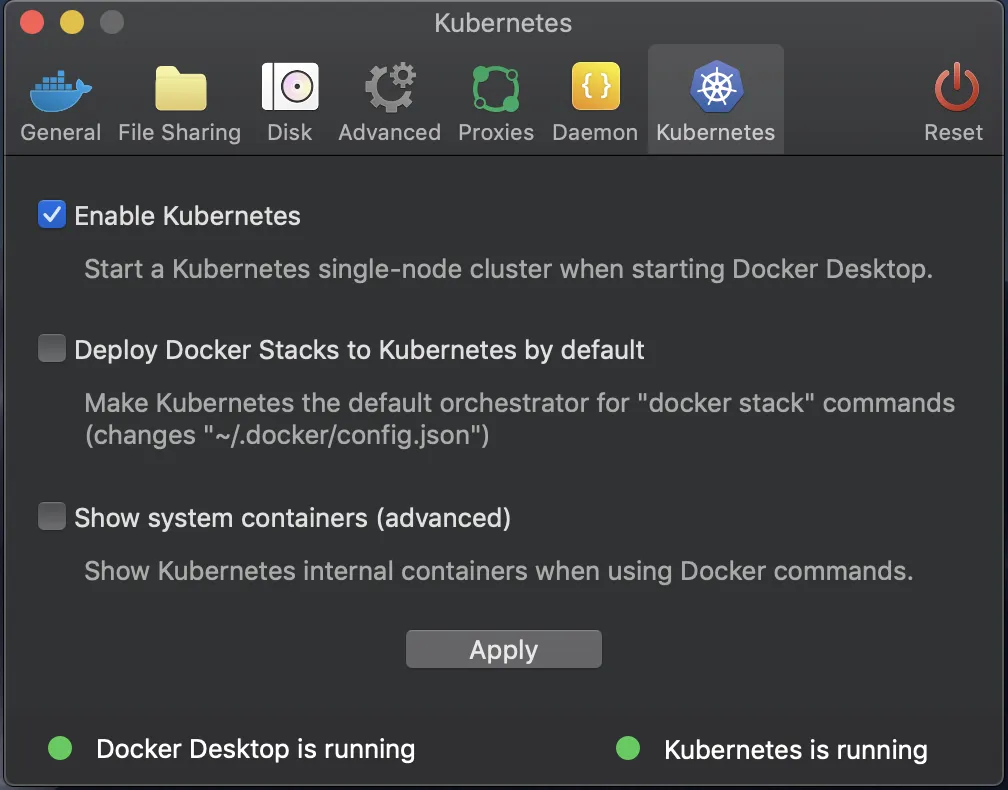 Depend on Docker for KubeflowDocker
 Revisiting Docker Hub Policies: Prioritizing Developer ExperienceDocker
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
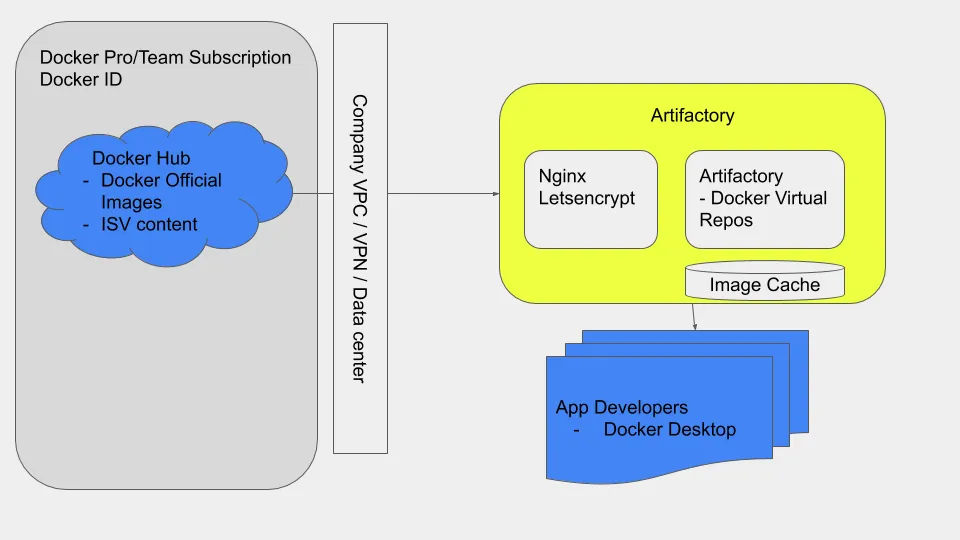 New Docker and JFrog Partnership Designed to Improve the Speed and Quality of App DevelopmentDocker
 How to Run Hugging Face Models Programmatically Using Ollama and TestcontainersDocker
 How AI Assistants Can Decode GitHub Repos for UI WritersDocker
 How to Colorize Pictures With OpenVINO™ on Ubuntu ContainersDocker
 Today Is The Day!Docker
