
The OWASP API Security Top Ten: API1:2019 Broken Object Level Authorization
The following (10 part!) blog series will be on the OWASP API Security Top Ten, 2019 version.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Semgrep × Cursor Hooks: Making Security Reliable for AgentsSemgrep
How we built an AppSec AI that security researchers agree with 96% of the timeSemgrep
Security AlertSemgrep
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 Docs-as-code solutions for API teams: how to choose the right platform in 2026Mintlify
 Redirects - MintlifyMintlify
 10 best AI observability tools for monitoring and evaluating agents in 2026Mintlify
 Who Explains the Most? An Analysis of Educational YouTubers - Deepgram Blog ⚡️Deepgram
 Top 3 Use Cases for Speech-to-Text in Gaming - Deepgram Blog ⚡️Deepgram
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
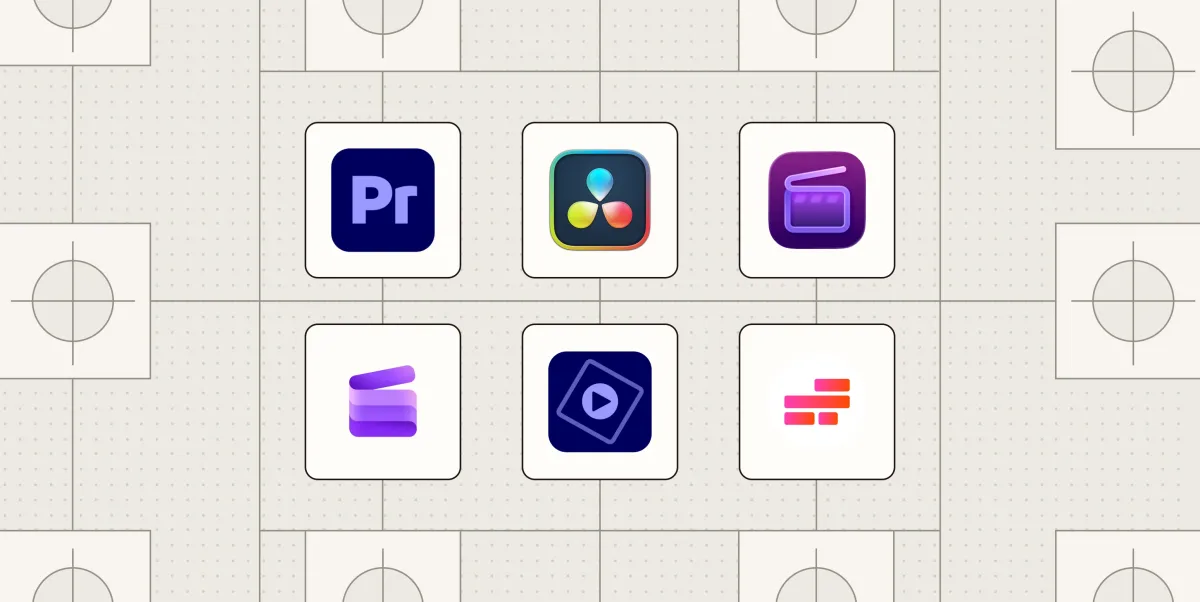 The Best Video Editing Software in 2026 (Including Free Options)Zapier
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
