
Understanding and mitigating the Log4Shell vulnerability
CVE-2021-44228, also known as Log4 Shell, is a remote code execution vulnerability in the Log4 j 2 library.
 Can LLMs Detect IDORs? Understanding the Boundaries of AI ReasoningSemgrep
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 Understanding Redis Enterprise Software Support PackagesRedis
 What are Logs and How are Logs Managed?Datadoghq
 Webinar Recap: Webinar Recap: Securing the Software Supply Chain with Docker BusinessDocker
 Understanding CSRF attacksVercel
 SuperGLUE: Understanding a Sticky Benchmark for LLMsDeepgram
 Context is Everything: Why Maximum Sequence Length Matters - CerebrasCerebras
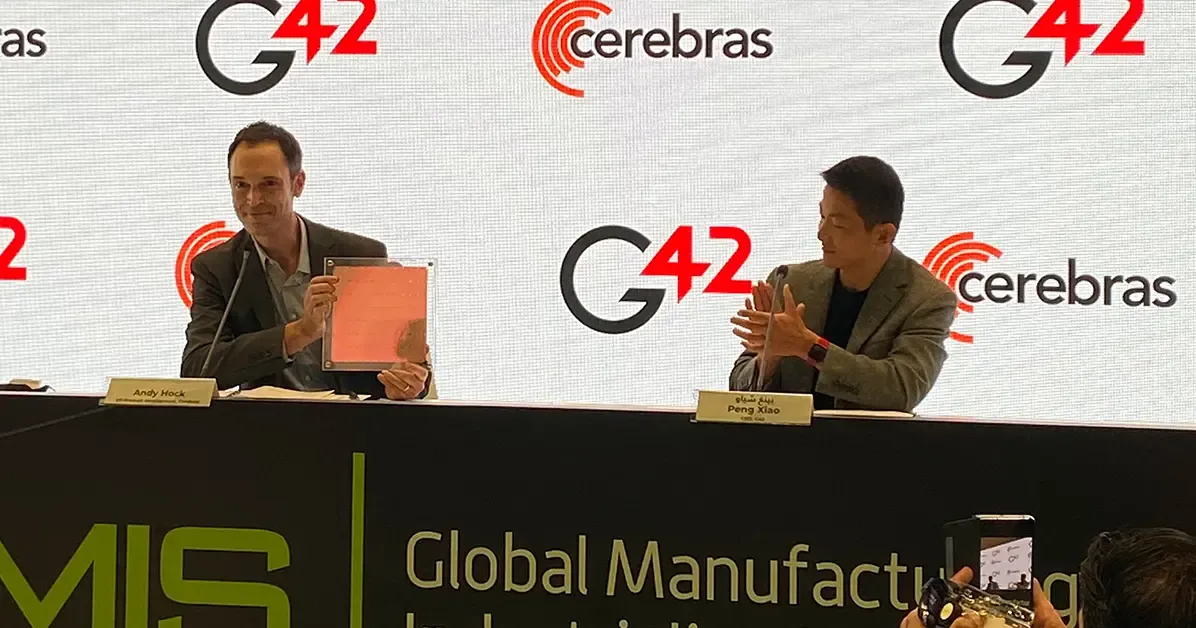 Cerebras Systems and G42 to Partner to Bring High-Performance AI Compute to the Middle EastCerebras
 Questions to Ask Your Hardened Image ProviderDocker
 Istio Certified Associate (ICA)Cncf
 Understanding React Server ComponentsVercel
 Generic ASR will never be accurate enough for Conversational AI - Deepgram Blog ⚡️Deepgram
 Vulnerability Scanning is BrokenSocket
 Unpacking the ROI of Coana's SCA With Reachability AnalysisSocket
 Socket Joins New OpenJS Program to Fund Node.js Security WorkSocket
