
You do not need to do DAST in a pipeline to do DevSecOps
The post also explains why DAST is not needed in your pipeline and encourages a tailored approach that fits an organization's unique needs rather than blindly following industry trends.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
 Workato integrations: What's included and when to use ZapierZapier
 Grafana Is Not Worried About AWS CommercializationThenewstack
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Inside the Go Playground - The Go Programming LanguageGo
 Do AI Agents Need a Semantic Layer?Motherduck
 The Anatomy of shadcn/ui ComponentsVercel
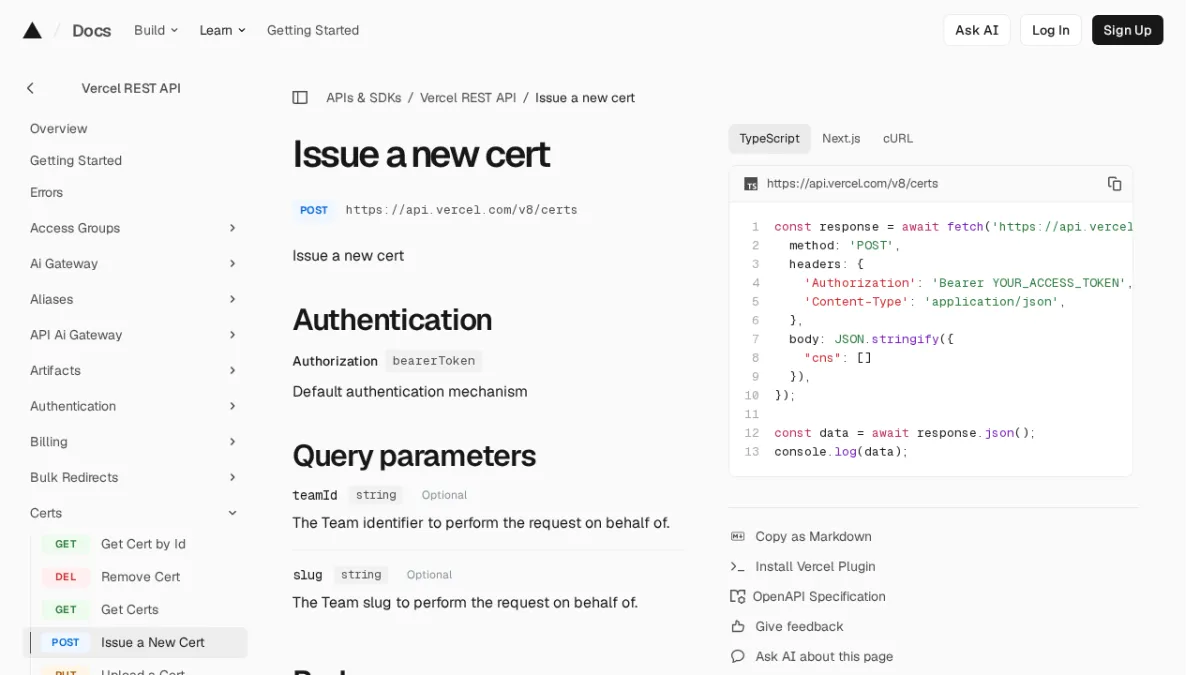 Issue a new certVercel
 From ASR to CSR: Why Conversation Changes EverythingDeepgram
 Real-Time Speech-to-Speech Translation: Architecture GuideDeepgram
 What You Need To Know About OpenAI’s New 3D Model-Making AI, Point-E - Deepgram Blog ⚡️Deepgram
 Configure OBI routes decoratorOpentelemetry
 How to instantly follow up on Facebook Lead Ads with custom notificationsZapier
 Inbox zero: What it is and how to actually get thereZapier
