
Your Window of Exposure is the Attacker's Window of Opportunity
Supply chain attacks succeed in a short window after release. Learn how attackers exploit that gap and practical steps to reduce your exposure.
 London calling: Highlights from the 2025 cloud & cyber security expoSemgrep
Boosting Security Scan Performance for Monorepos with Multicore Parallel ProcessingSemgrep
Beyond Benchmarks: How Semgrep Redefines Javascript SecuritySemgrep
Benchmarking Semgrep Community Edition Performance ImprovementsSemgrep
Beyond vulnerabilities: Detect malicious dependencies in your supply chainSemgrep
 The stack overflow of death. Why we were down for 2 hoursBunny
 A “new direction” in the struggle against rightward scrollingCss Tricks
 Transient activation - GlossaryDeveloper Mozilla
 Elastic at Gartner IT Symposium/Xpo 2025Elastic
 Elastic Security at Black Hat 2026Elastic
 Elastic at RSACElastic
 The Magic of In-Person FeedbackNotion So
 Compiling Qt with Docker multi-stage and multi-platformDocker
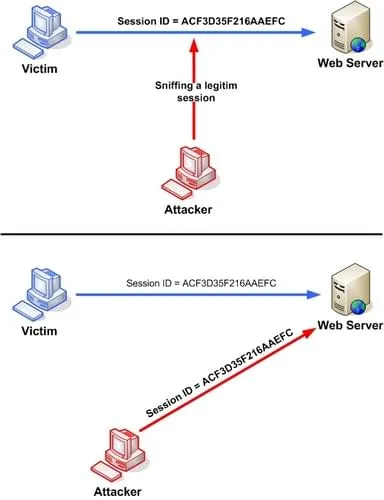 Session hijacking - GlossaryDeveloper Mozilla
 Sticky activation - GlossaryDeveloper Mozilla
 Demo On DemandTurn SaaS and AI sprawl into opportunity1password
 RANK and DENSE_RANKMotherduck
 ChatGPT automation: How to use the Zapier ChatGPT integrationZapier
 AWS PrivateLink for Neon Databases - NeonNeon
