
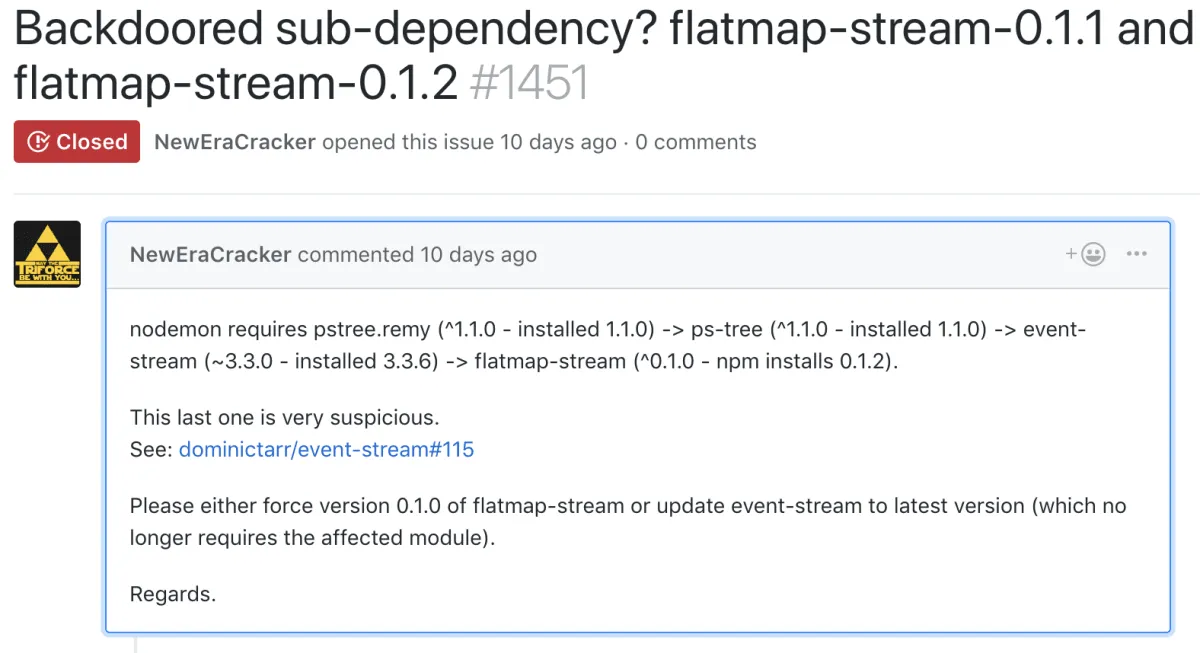
A post-mortem of the malicious event-stream backdoor
A look back at the chain of events that led to the use of the malicious npm package "flatmap-stream" and a reflection on what it means for the fragility of open source.
 Weaponizing AI Coding Agents for Malware in the Nx Malicious Package Security IncidentSnyk
What is a Container Registry security?Snyk
10 best practices to containerize Node.js web applications with DockerSnyk
How to verify and secure your Mastodon accountSnyk
Vulnerability assessmentSnyk
Using Snyk reporting for data-driven securitySnyk
 Three Key Design Considerations for an Event-Driven ArchitectureThenewstack
 New Policy as Code Capabilities with CrossGuardPulumi
 Pseudo-Randomly Adding Illustrations with CSS | CSS-TricksCss Tricks
 Practical Uses for AI in Your Data WorkflowsMotherduck
Data Council 2025Motherduck
Ship It: Dinner & Drinks on a BoatMotherduck
Spatial Data Management with DuckDB ft. MattForrestMotherduck
MotherDuck Builder Office Hours - July 21Motherduck
Duck Duck Stream: How to Efficiently Load Data into DuckLake with EstuaryMotherduck
Data Rock N' Roll at AWS re:InventMotherduck
NL dbt meetup: 14th EditionMotherduck
Blood, Sugar, Hex, Magic WednesdayMotherduck
SQL is Dead, Long Live SQL: Engineering a Reliable Analytics Agent from ScratchMotherduck
dbt Coalesce 2025Motherduck
