
Creating SBOMs with the Snyk CLI
Creating SBOMs with the Snyk CLI February 5, 2025 0 mins read The software bill of materials (SBOM) is quickly becoming an essential aspect of open source security and compliance.
 Playing With P5.js: Creating a Voice-Controlled Game - Deepgram Blog ⚡️Deepgram
 CLI ReferenceModal
 Creating Color Themes With Custom Properties, HSL, and a Little calc()Css Tricks
 Docker Desktop 4.18: Docker Scout Updates, Container File Explorer GADocker
 Creating an AI Summary App with Next.js | Vercel AcademyVercel
 6 tips every developer should know when using Cursor and Windsurf AIMintlify
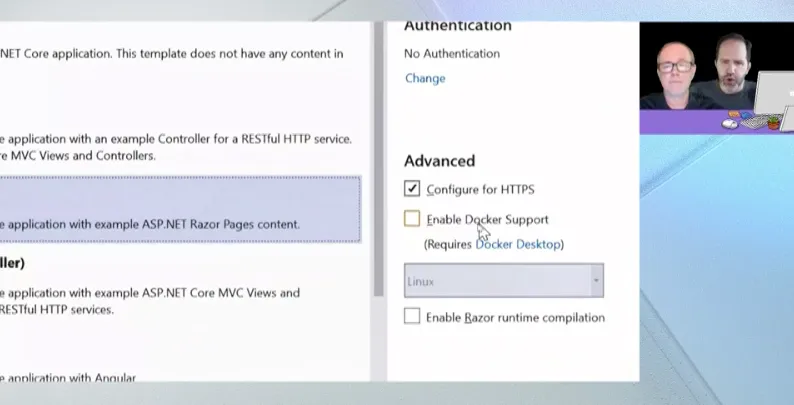 Creating the best Linux Development experience on Windows & WSL 2 | DockerDocker
 Streamline NGINX Configuration with Docker Desktop ExtensionDocker
 Step-by-Step Guide to Creating Face Swap Videos with HeyGenHeygen
 Mintlify CLI - MintlifyMintlify
 No More Zapier Timeouts: Transcribe Large Audio Files with Deepgram and Zapier’s WebhooksDeepgram
 4 ways to automate Personal AIZapier
 Introducing Socket OptimizeSocket
 Fiberplane’s Collaborative Notebooks for Incident ManagementThenewstack
