
CVE-2025-29927 Authorization Bypass in Next.js Middleware | Snyk
On Friday morning, March 21, 2025, at 9:00 a.m. UTC, a security advisory identified as CVE-2025-29927 was published.
 Trigger automation - MintlifyMintlify
 Trained on 100,000+ Voices: Deepgram Unveils Next-Gen Speaker Diarization and Language DetectionDeepgram
 Q&A with Deepgram’s New CPO, Ed AnuffDeepgram
 Intel Unveils Next Generation Neuromorphic Computing ChipThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Data Council 2025Motherduck
dbt Coalesce 2025Motherduck
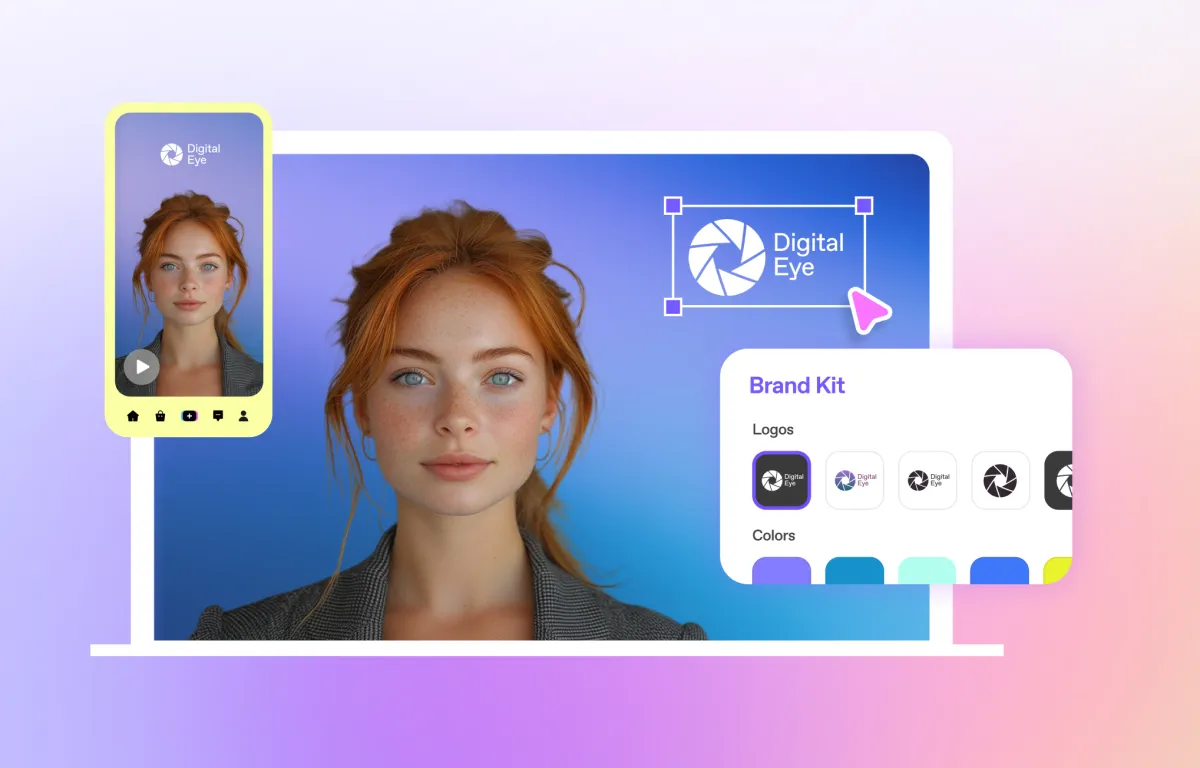 How to Make AI Videos Look Professional in 2025Heygen
 20 Must-Attend Startup Events in San Francisco 2025 | HeyGenHeygen
 Creating an AI Summary App with Next.js | Vercel AcademyVercel
 AGENTS.md outperforms skills in our agent evalsVercel
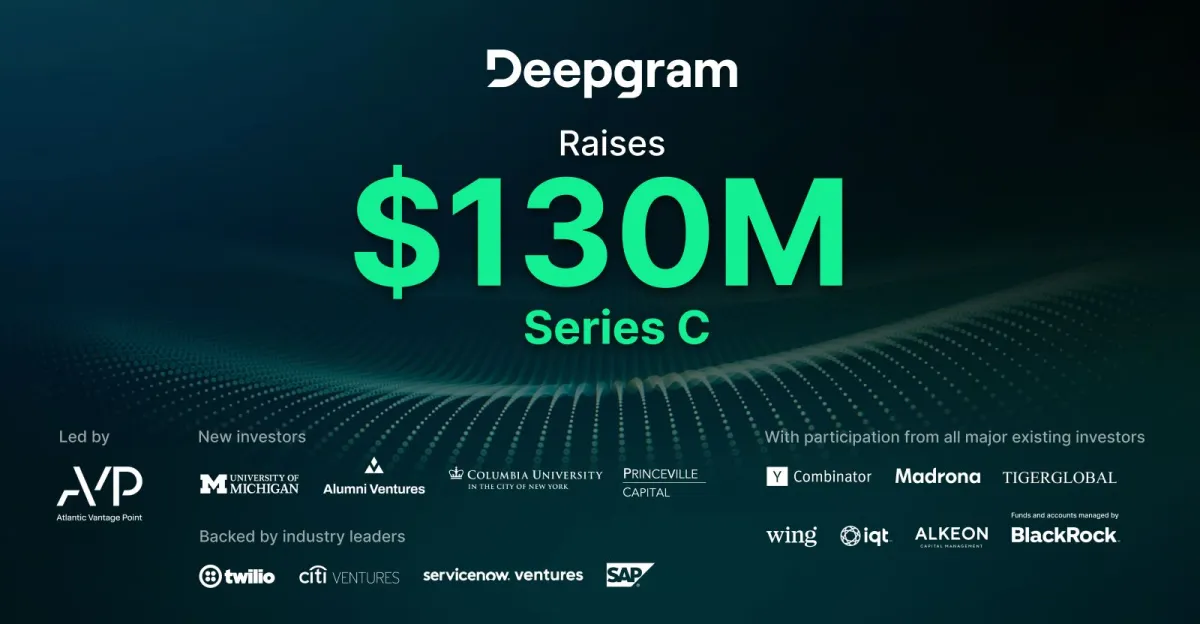 Today We Start the Next Chapter of the Voice AI EconomyDeepgram
 Configure OBI routes decoratorOpentelemetry
 Next-level IaC: Powering Up Pulumi with Package EcosystemsPulumi
