
Dependency Health—assessing package risk with Snyk
Snyk’s goal is to help you use open source in a secure way. Vulnerabilities are one indicator that a dependency is unhealthy, but there are other risk factors at play as well.
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Go Concurrency Patterns: Context - The Go Programming LanguageGo
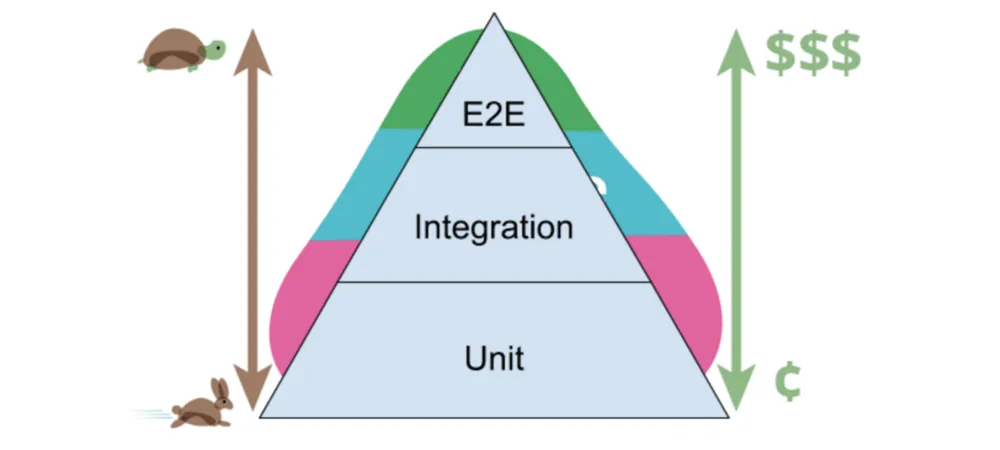 Develop, Preview, TestCss Tricks
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Introducing Dependency Divergence GitHub ActionSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 Next-level IaC: Powering Up Pulumi with Package EcosystemsPulumi
 Announcing dependency caching for Pulumi DeploymentsPulumi
Forward Compatibility and Toolchain Management in Go 1.21 - The Go Programming LanguageGo
 Webinar: Migrate from Legacy Platforms to Datadog with AeginDatadoghq
 Docker Scout health scores: Security grading for container images in your Docker Hub registryDocker
 Mental Health Marketing: A Responsible 2026 GuideHeygen
 Troubleshooting Python automatic instrumentation issuesOpentelemetry
 Third-Party Risk Management (TPRM): A Complete GuideZapier
