
Ensuring comprehensive security testing in DevOps pipelines
Learn how to integrate comprehensive security testing into DevOps pipelines to protect your entire software development lifecycle.
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 When CI Meets CD: Deliver With ConfidenceThenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 Platform Engineering & DevOps Series Kickoff AnnouncementPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 Supporting Kubernetes with Faster, Easier Test EnvironmentsPulumi
 Go Concurrency Patterns: Pipelines and cancellation - The Go Programming LanguageGo
 Anthropic integration with Modal brings scalable compute to Claude ScienceModal
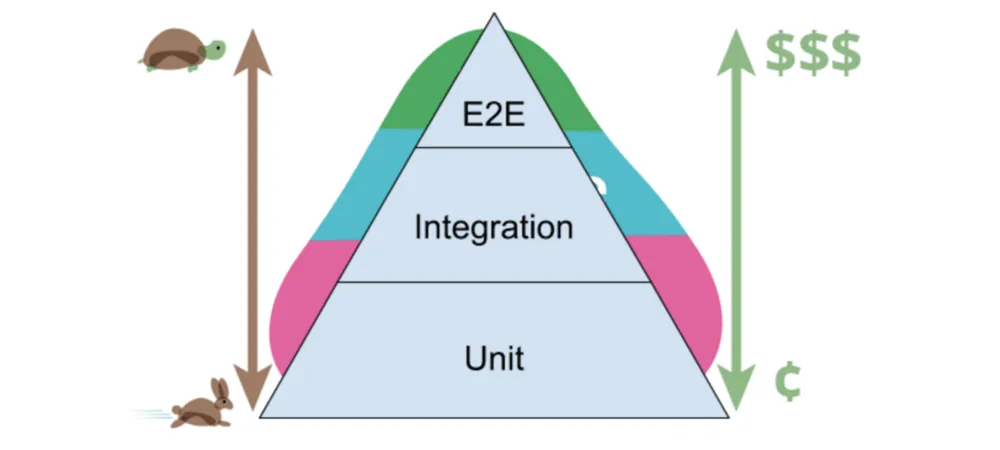 Develop, Preview, TestCss Tricks
