
Exploring CVE-2022-33980: the Apache Commons configuration RCE vulnerability
However, we want to make it clear that there’s no need for panic. This is simple configuration manipulation.
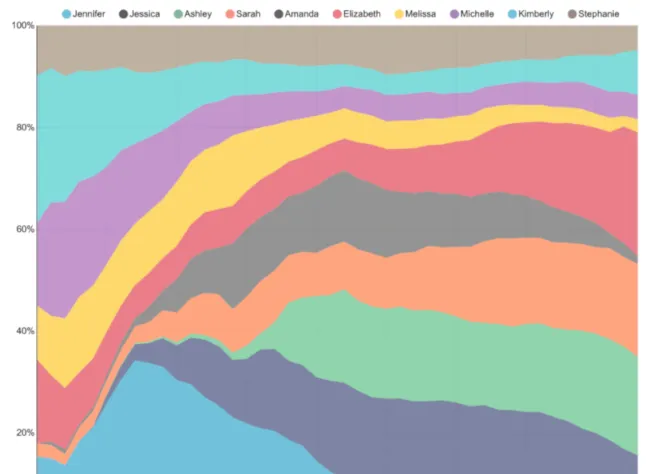 Explore and Visualize Data the Apache Superset WayThenewstack
 Pulumi ESC Table Editor Now Supports Dynamic Credential and Secret IntegrationsPulumi
 Pushing Pulumi ESC Secrets into External PlatformsPulumi
 The Go Memory Model - The Go Programming LanguageGo
 Automatic cipher suite ordering in crypto/tls - The Go Programming LanguageGo
 Cerebras Systems Enables GPU-Impossible™ Long Sequence Lengths Improving Accuracy in NaturalCerebras
 Docker Desktop 4.23: Updates to Docker Init, New Configuration Integrity Check, Quick SearchDocker
 How AI Assistants Can Decode GitHub Repos for UI WritersDocker
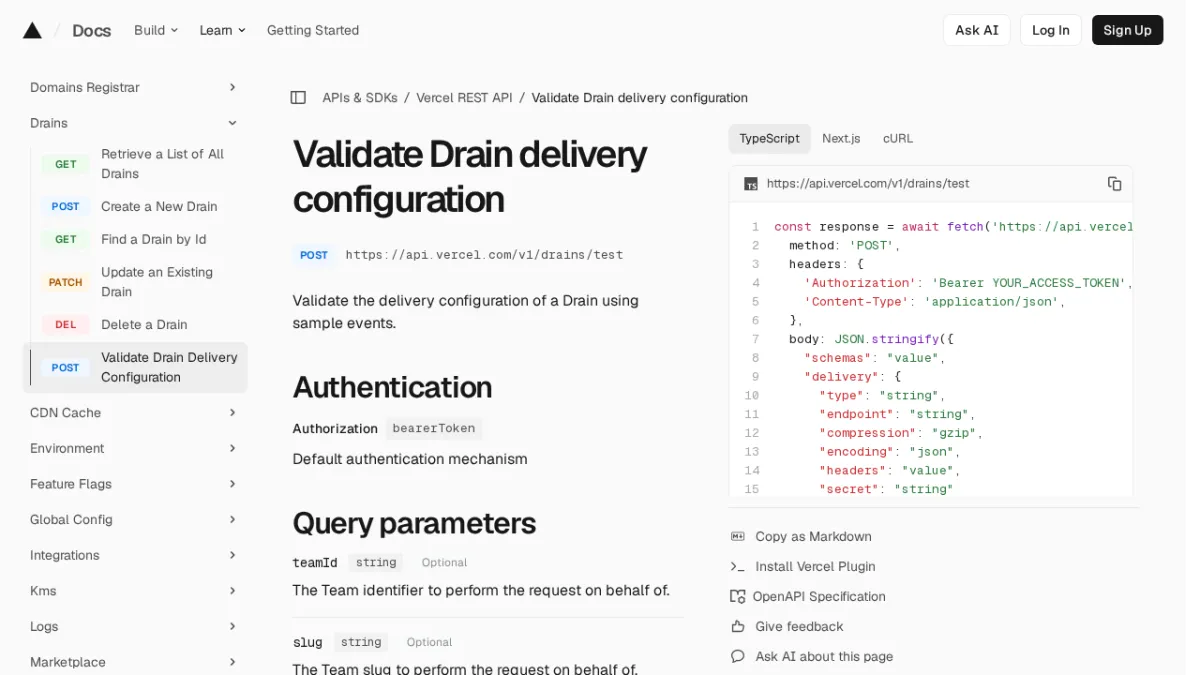 Validate Drain delivery configuration | Vercel REST APIVercel
 ESLINT_CONFIGURATIONVercel
 View - MintlifyMintlify
 .NET Framework instrumentation configurationOpentelemetry
ConfigurationOpentelemetry
Instrumentation configurationOpentelemetry
