
Find and fix HTTP/2 rapid reset zero-day vulnerability CVE-2023-44487
HTTP/2 rapid reset vulnerability is being tracked as CVE-2023-44487, assigned High severity.
 How we grew Mintlify by doing things that don't scaleMintlify
 Rapid `14 Q1 Growth, 23K+ Customers, 45K+ Instances, 4 Clouds (and 10 Regions)Redis
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 Go.dev: a new hub for Go developers - The Go Programming LanguageGo
From zero to Go: launching on the Google homepage in 24 hours - The Go Programming LanguageGo
 How Ramp automated receipt processing with fine-tuned LLMsModal
 CSS Hell | CSS-TricksCss Tricks
 It's Ducking Easy: From Zero to Insight with MotherDuck and dbtMotherduck
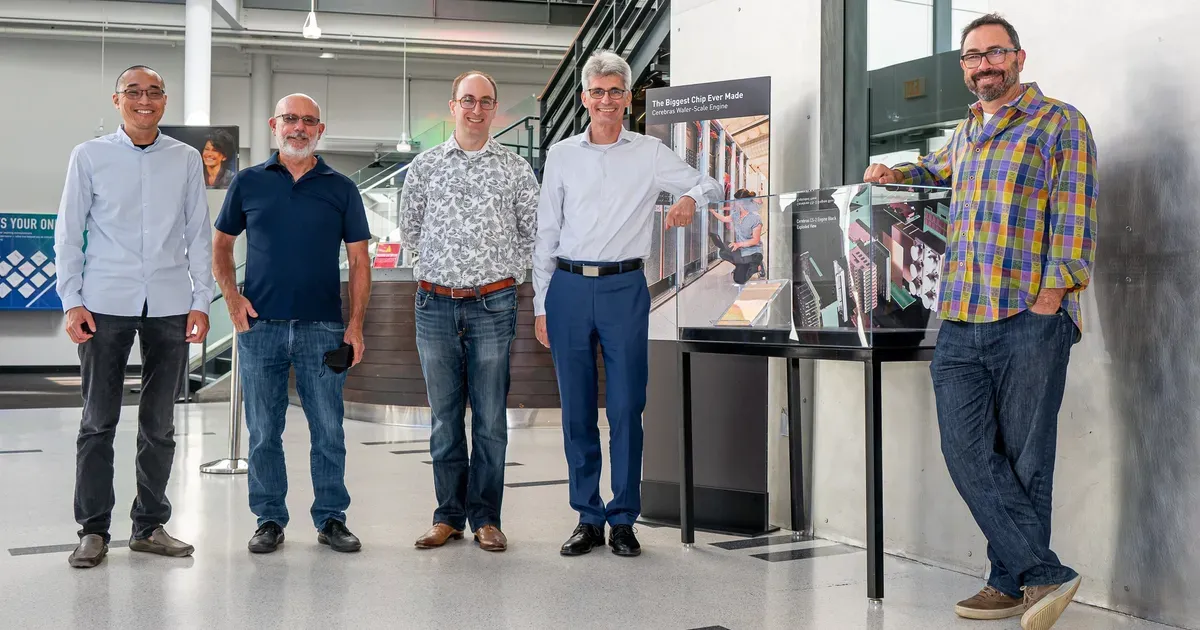 Cerebras Wafer-Scale Engine Inducted into the Computer History Museum - CerebrasCerebras
 Today Is The Day!Docker
 How the world’s biggest YouTuber served millions of users on VercelVercel
 ESLINT_CONFIGURATIONVercel
 Iterating from design to deploy: Guillermo Rauch's talk at Figma Config 2023Vercel
 Launch Week II Day 2: Snippets V2Mintlify
