
Finding and fixing exposed hardcoded secrets in your GitHub project with Snyk
In this blog, we'll show how you can use Snyk to locate hardcoded secrets and credentials and then refactor our code to use Doppler to store those secrets instead.
 Video: Building a Live Transcription Badge With Deepgram - Deepgram Blog ⚡️Deepgram
 Integrate Jupyter Notebooks with GitHubThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Pulumi Neo Now Supports AGENTS.mdPulumi
 Pushing Pulumi ESC Secrets into External PlatformsPulumi
 How AI Assistants Can Decode GitHub Repos for UI WritersDocker
 Docker Desktop 4.18: Docker Scout Updates, Container File Explorer GADocker
 vercel flagsVercel
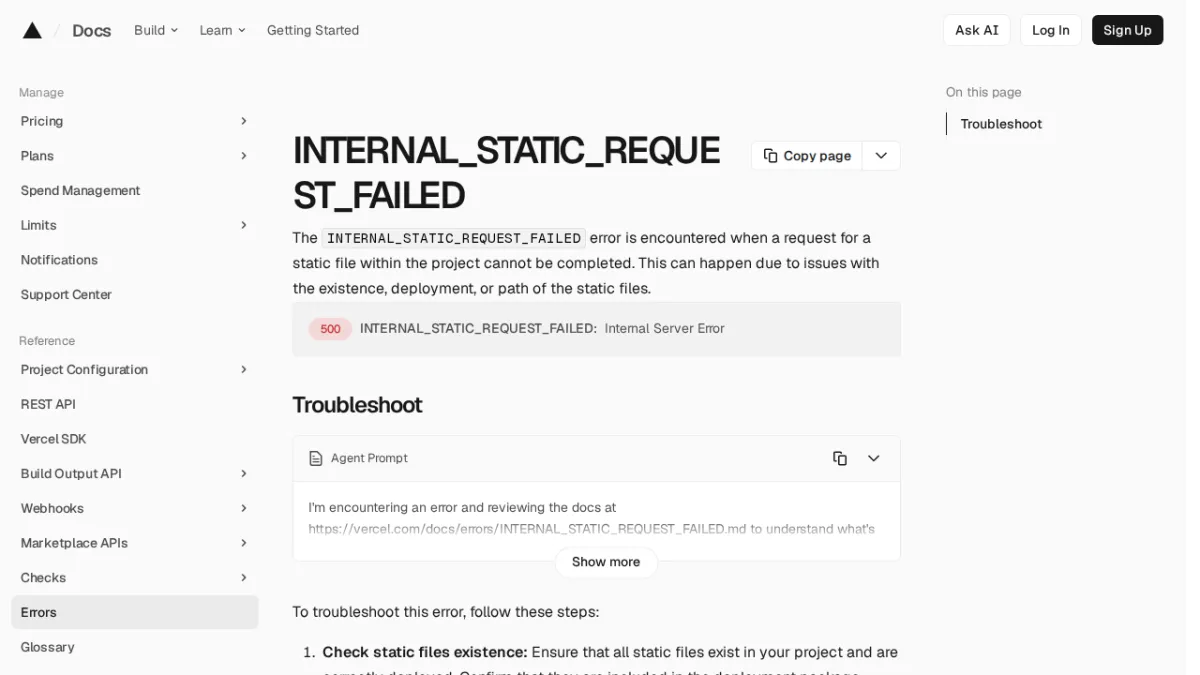 INTERNAL_STATIC_REQUEST_FAILEDVercel
 Build Your Own PluginVercel
 Using Web AnalyticsVercel
 GitHub - MintlifyMintlify
 Introducing AI AssistantMintlify
