
Fixing SQL Injection: ORM is not enough
Using a programmable SQL interface such as an ORM (Object Relational Mapping) is a good way to reduce risk of SQL Injection, which is a very bad vulnerability to have.
 Grafana Is Not Worried About AWS CommercializationThenewstack
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 Inside the Go Playground - The Go Programming LanguageGo
 Analyze JSON Data Using SQL and DuckDBMotherduck
 Summer Data Engineering RoadmapMotherduck
 SQL is Dead, Long Live SQL: Engineering a Reliable Analytics Agent from ScratchMotherduck
 The Anatomy of shadcn/ui ComponentsVercel
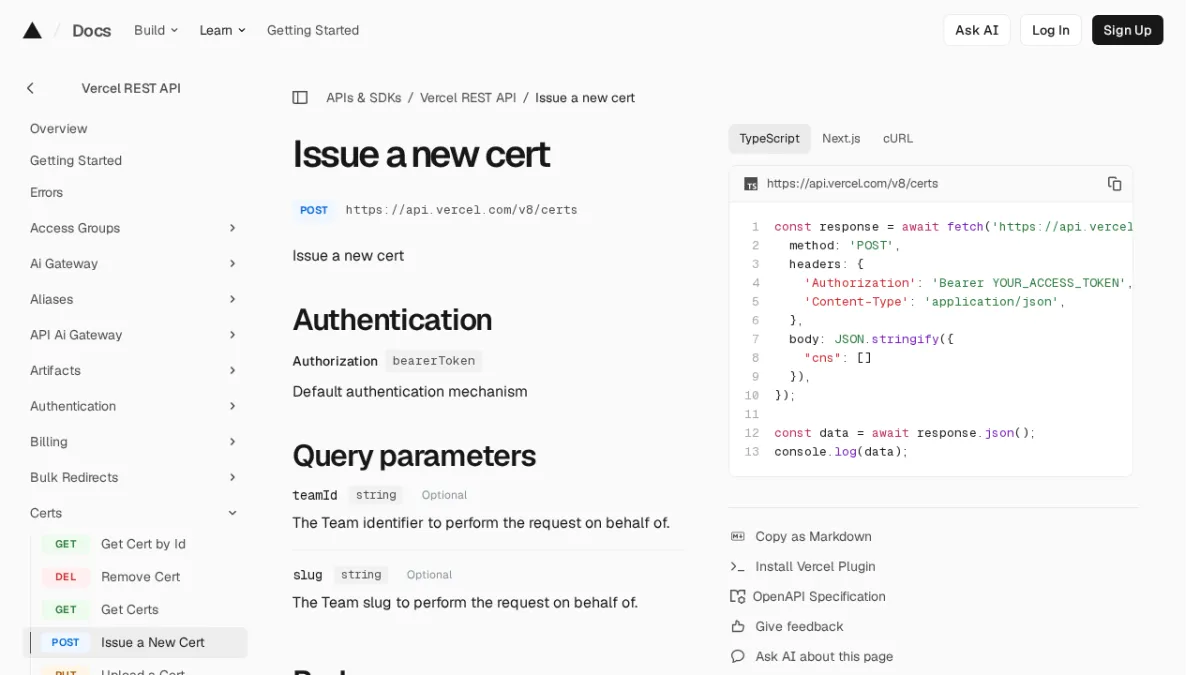 Issue a new certVercel
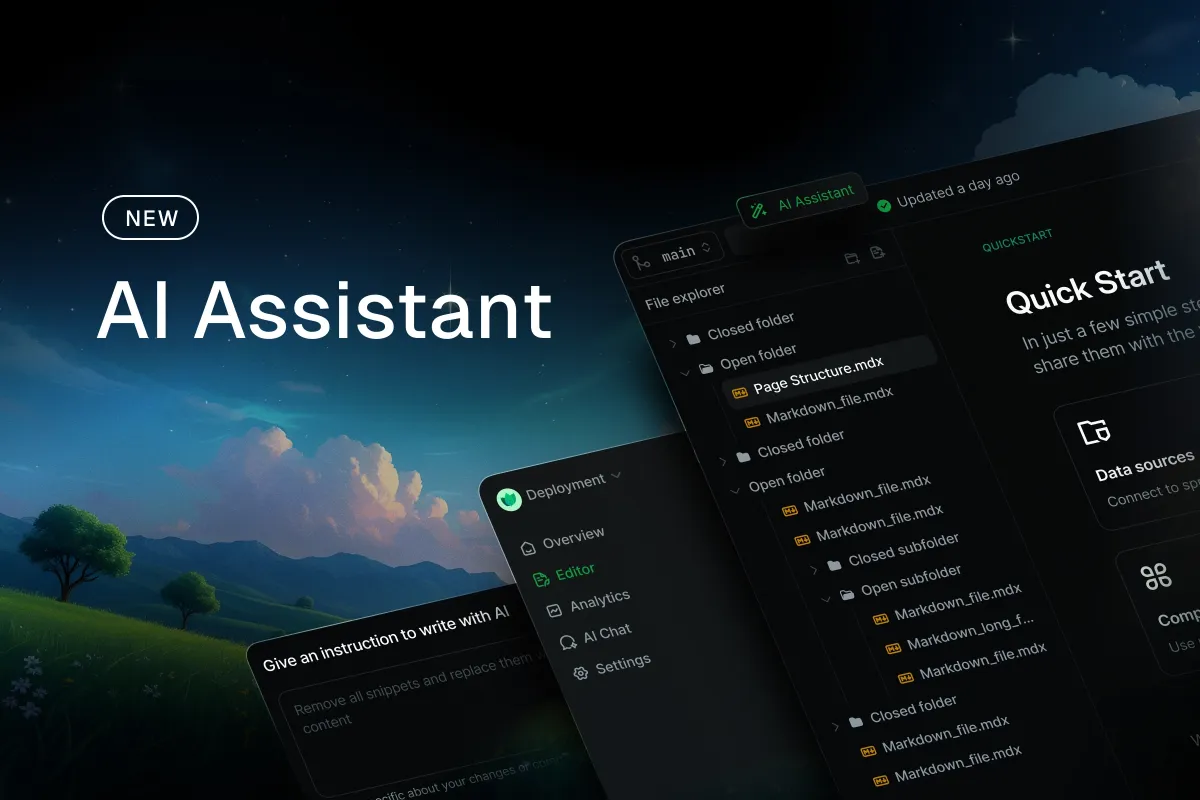 Introducing AI AssistantMintlify
 Training: Hard Work Pays off for Data/AI ProsThenewstack
 Your Perfect Infrastructure May Not Be So PerfectPulumi
 Effective Go - The Go Programming LanguageGo
 Defining “View Source”Css Tricks
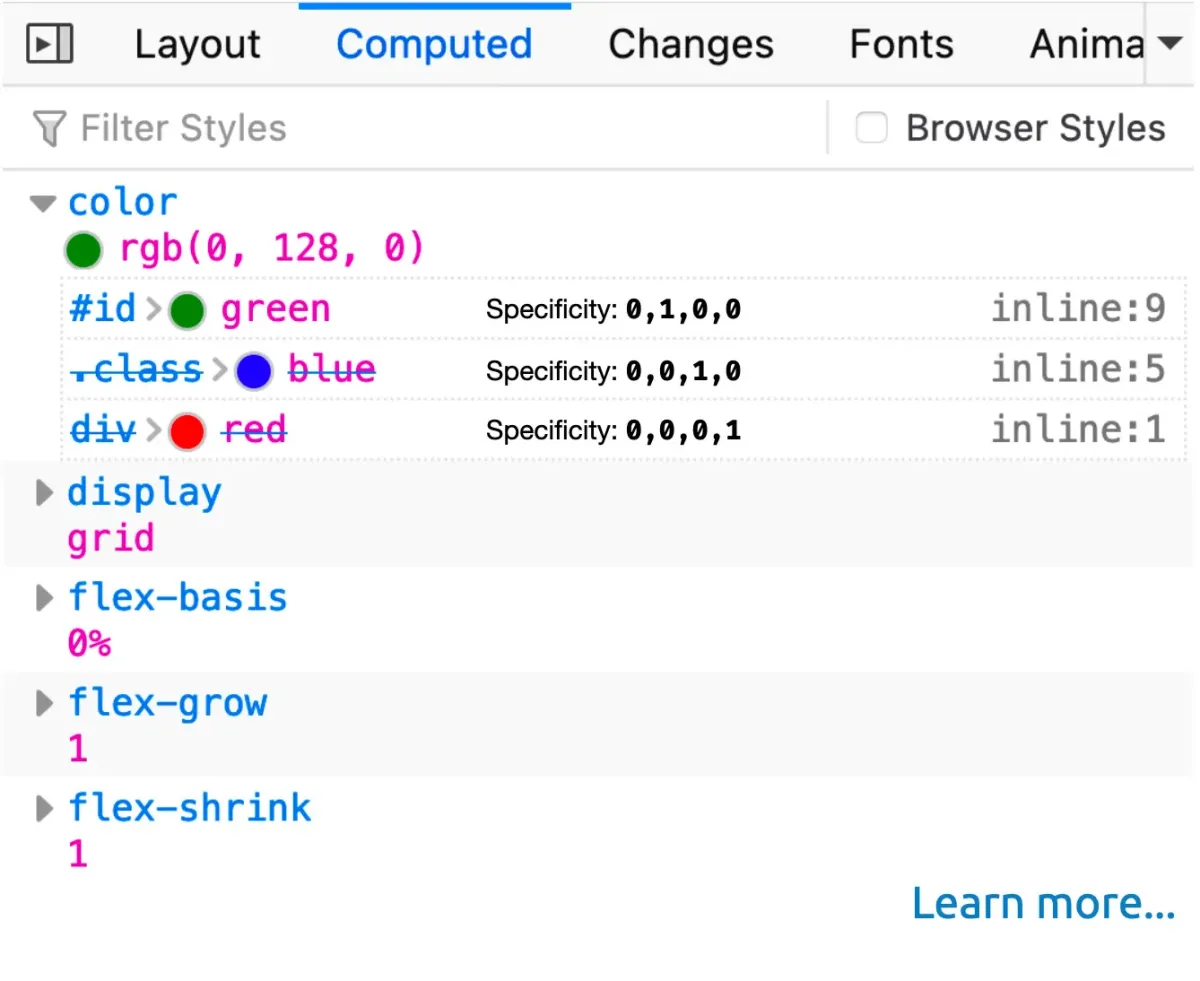 Should DevTools teach the CSS cascade?Css Tricks
