
Java JSON deserialization problems with the Jackson ObjectMapper
Learn how Jackson ObjectMapper deserialization vulnerabilities work and how to make sure you are not affected by them.
 Redirects - MintlifyMintlify
 Analyze JSON Data Using SQL and DuckDBMotherduck
 Supporting the jsDelivr open source CDN with bandwidth for developersBunny
 ESLINT_CONFIGURATIONVercel
 JS plain objects compiler pluginKotlinlang
HTML | KotlinKotlinlang
Calling Java from KotlinKotlinlang
 OpenAI Chat Completions Structured Outputs with AI GatewayVercel
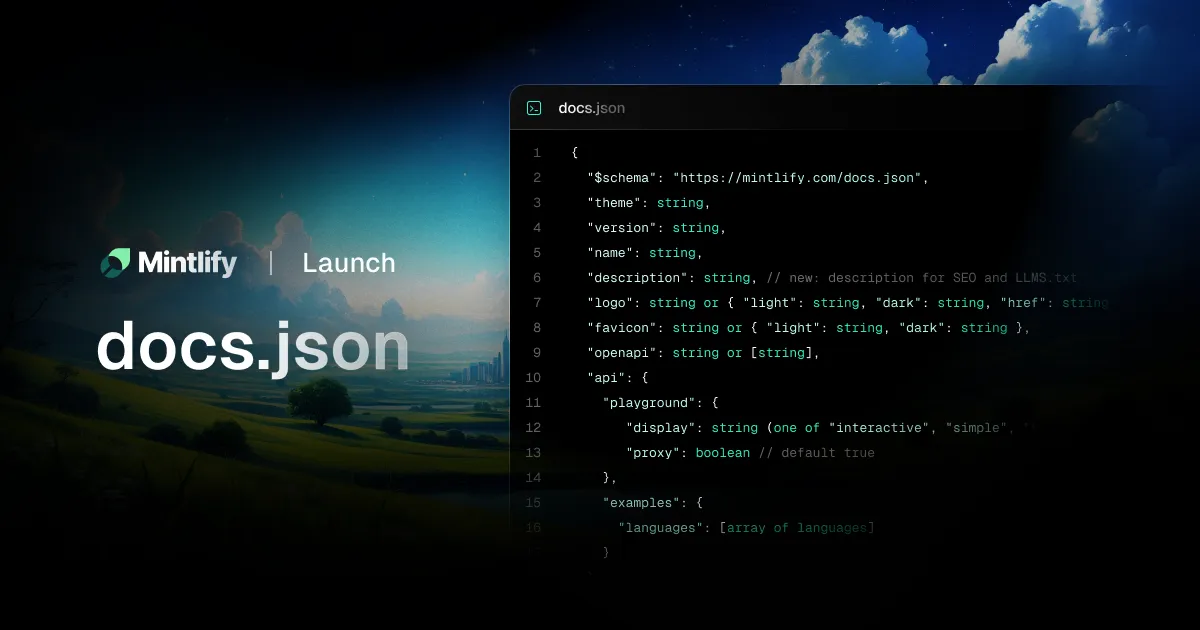 Refactoring mint.json into docs.jsonMintlify
 Cleaning up import paths in JS/TS packagesSocket
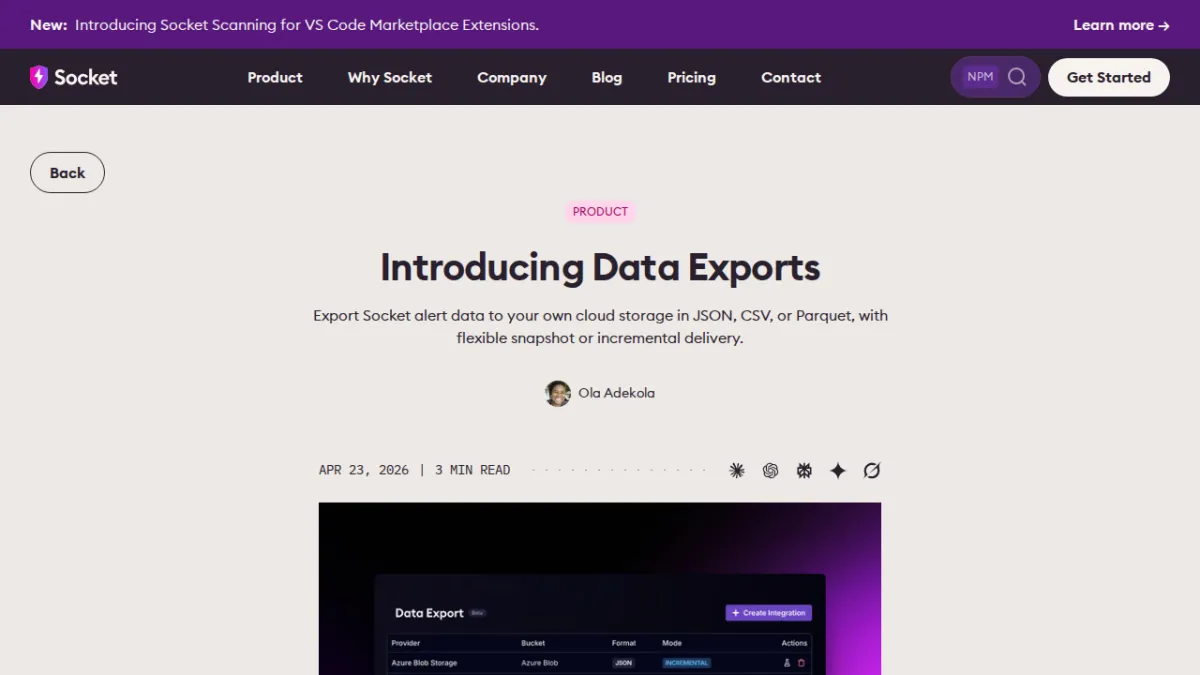 Introducing Data ExportsSocket
 Documentation - JS Projects Utilizing TypeScriptTypescriptlang
Documentation - What is a tsconfig.jsonTypescriptlang
 Pulumi Release Notes: Colorized Stack Traces, Output Methods for JSON, OIDC integration, and muchPulumi
