
Lessons from OpenSSL vulnerabilities part 1: Preparing your supply chain for the next critical
In this two part series, we'll walk through some of the things you need to consider when finding instances of a vulnerability in your software supply chain.
 Trigger automation - MintlifyMintlify
 Trained on 100,000+ Voices: Deepgram Unveils Next-Gen Speaker Diarization and Language DetectionDeepgram
 Playing With P5.js: Creating a Voice-Controlled Game - Deepgram Blog ⚡️Deepgram
 Calling Your Video Game With Your Phone: Part 1Deepgram
 Q&A with Deepgram’s New CPO, Ed AnuffDeepgram
 An Introduction to Redis-ML. Part OneRedis
 How to connect Google Sheets to NotionZapier
 Intel Unveils Next Generation Neuromorphic Computing ChipThenewstack
 Lessons Swift Designer Chris Lattner Has Learned about LeadershipThenewstack
 Announcing Restore Stacks: Recover Deleted Stacks in the Pulumi CloudPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 New Policy as Code Capabilities with CrossGuardPulumi
 Module version numbering - The Go Programming LanguageGo
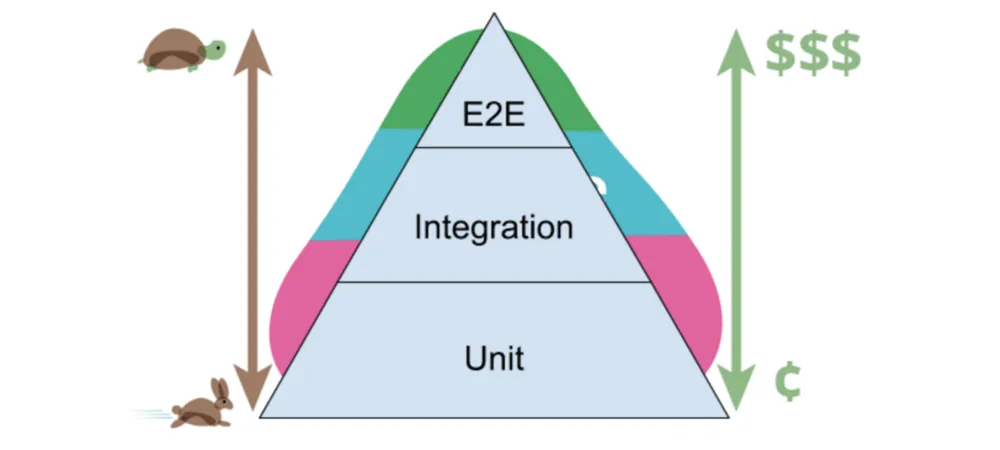 Develop, Preview, TestCss Tricks
