
Log4j 2.15 Vulnerability Cve-2021-45046 Upgraded To A Critical Severity Arbitrary Code Execution
It has been discovered that Log4j version 2.15.0 is still susceptible to arbitrary code execution (CVE-2021-45046) in certain circumstances.
 Docs-as-code solutions for API teams: how to choose the right platform in 2026Mintlify
 Mintlify Alternatives: What to Consider (and Why There's No True Substitute)Mintlify
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 No Code Transcription: Simplifying Workflows with Deepgram and Make.comDeepgram
 How to connect Google Sheets to NotionZapier
 Oso Unbundles Security AuthorizationThenewstack
 Empower Your Team with Policy as CodePulumi
 Announcing Restore Stacks: Recover Deleted Stacks in the Pulumi CloudPulumi
 Five Years of Infrastructure as CodePulumi
 New Policy as Code Capabilities with CrossGuardPulumi
 Godoc: documenting Go code - The Go Programming LanguageGo
 Managing dependencies - The Go Programming LanguageGo
 How Hunch supercharged AI workflows with Modal SandboxesModal
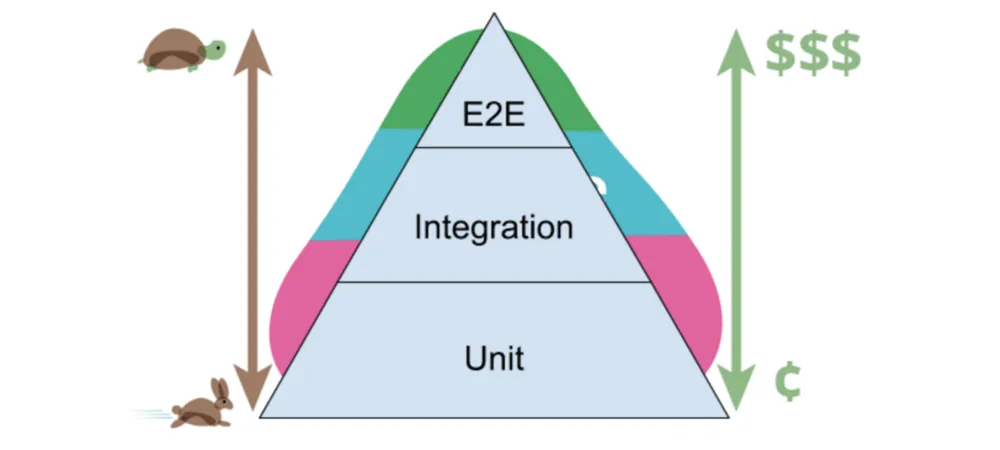 Develop, Preview, TestCss Tricks
