
Log4j 2.16 High Severity Vulnerability (CVE-2021-45105) Discovered
Overnight, it was disclosed by Apache that Log4j version 2.16 is vulnerable by way of a Denial of Service attack with the impact being a full application crash.
 Tagalog Speech to TextDeepgram
 Discovered Stacks: One Place for All Your InfrastructurePulumi
 AMD and Cerebras Announce Disaggregated AI InferenceCerebras
 How to Make AI Videos Look Professional in 2025Heygen
Kannada Speech to TextDeepgram
 What's new at Zapier: December 2021Zapier
 How to use automation to close high value dealsZapier
 Pulumi Context API: query your infrastructure as a graphPulumi
 Webinar: Migrate from Legacy Platforms to Datadog with AeginDatadoghq
 Cerebras Systems and National Energy Technology Laboratory Set New Milestones for High-PerformanceCerebras
 Cerebras Systems Sets Record for Largest AI Models Ever Trained on A Single Device - CerebrasCerebras
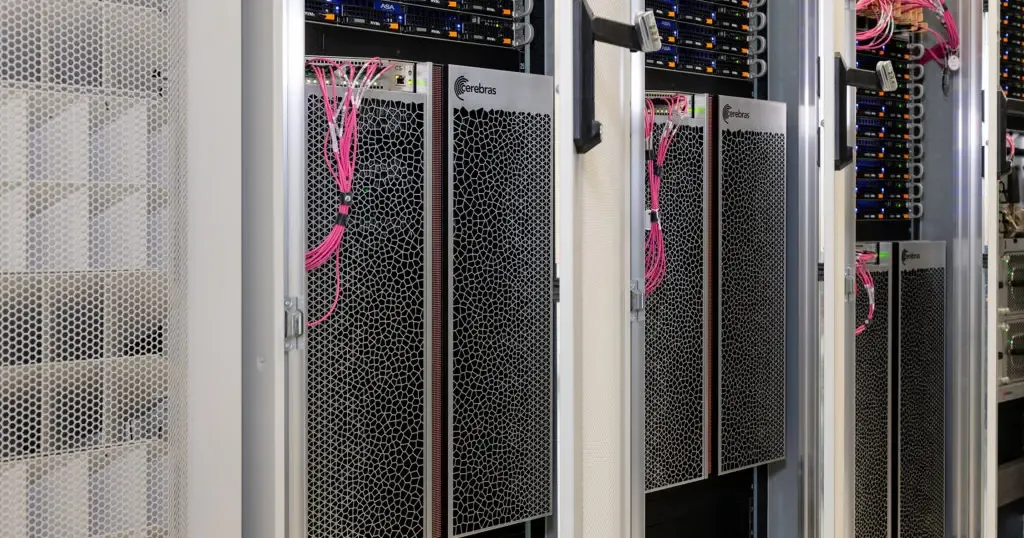 Cirrascale Cloud Services® and Cerebras Systems Announce Availability of Cerebras Cloud @ CirrascaleCerebras
 Cerebras Is Coming to AWS Bedrock for Fast AI InferenceCerebras
 Announcing the Cerebras Architecture for Extreme-Scale AI - CerebrasCerebras
