
Malicious Release of elementary-data PyPI Package Steals Cloud Credentials from Data Engineers
Attackers exploited a GitHub Actions script injection vulnerability to publish a malicious version of the elementary-data Python CLI (v0.23.3), embedding a credential-stealing backdoor that targeted dbt profiles, cloud provider keys, and SSH secrets from data engineering environments.
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Digital Forensics & Emerging Technologies GuideCybersecurity Exchange
 State of Speech: Our New Data Report Reveals ASR’s Untapped Potential - Deepgram Blog ⚡️Deepgram
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 The Most Important Work in AI Training Is Also the Most Overlooked - Deepgram Blog ⚡️Deepgram
 New Spanish and Turkish Language Models and Updated General Models - Deepgram Blog ⚡️Deepgram
 Redis Cloud PrivateRedis
Data Ingestion: 6 Ways to Speed Up Your ApplicationRedis
 5 ways to automate Browse AIZapier
 How to connect Google Sheets to NotionZapier
 This Week in Programming: Who's Headed to KubeCon?Thenewstack
 Pancakes Are Delicious and Data Centers Are for Free StuffThenewstack
 Puppet’s New Mission: Automating Cloud Native InfrastructureThenewstack
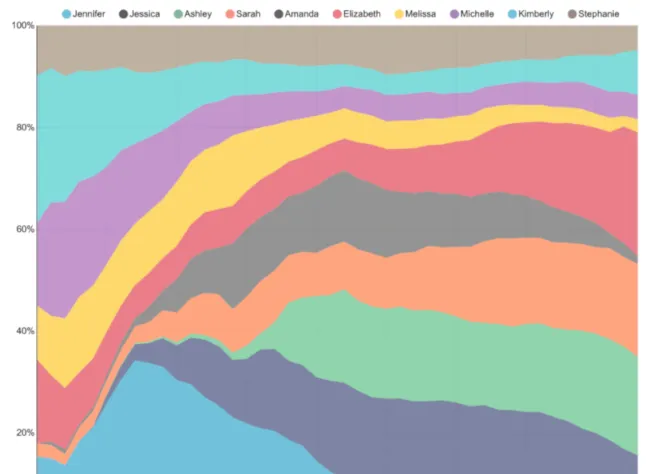 Explore and Visualize Data the Apache Superset WayThenewstack
