
Malicious remote code execution backdoor discovered in the popular bootstrap-sass Ruby gem
On March 26, 2019, a malicious version of the popular bootstrap-sass package, that has been downloaded a total of 28 million times to date, was published to the official RubyGems repository.
 Docs-as-code solutions for API teams: how to choose the right platform in 2026Mintlify
 Mintlify Alternatives: What to Consider (and Why There's No True Substitute)Mintlify
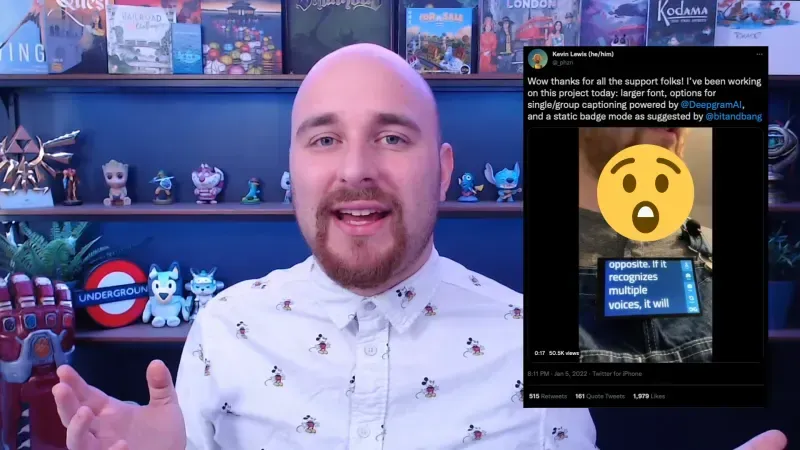 Video: Building a Live Transcription Badge With Deepgram - Deepgram Blog ⚡️Deepgram
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 No Code Transcription: Simplifying Workflows with Deepgram and Make.comDeepgram
 Automate Audio Transcription with Zapier + DeepgramDeepgram
 Grafana Is Not Worried About AWS CommercializationThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Empower Your Team with Policy as CodePulumi
 AWS Enterprise Container Management with PulumiPulumi
 Discovered Stacks: One Place for All Your InfrastructurePulumi
 Five Years of Infrastructure as CodePulumi
 New Policy as Code Capabilities with CrossGuardPulumi
 Godoc: documenting Go code - The Go Programming LanguageGo
