
ReDoS vulnerabilities in npm spikes by 143% and XSS continues to grow
Regex for for a single-threaded runtime could be devastating. We’ve also detected that the npm ecosystem has seen the most XSS vulnerabilities, Maven Central and PyPI follow next.
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 Happy Birthday, Shai-HuludSocket
 amoCRM: App of the dayZapier
 How to Protect Your Projects from the Risks of Deprecated npm PackagesSocket
 When "Everything" Becomes Too Much: The npm Package Chaos of 2024Socket
 Popular npm Packages in the keyv and Cacheable Namespaces Compromised in Active Supply Chain AttackSocket
 Cleaning up import paths in JS/TS packagesSocket
 Supply Chain Attack on Axios Pulls Malicious Dependency from npmSocket
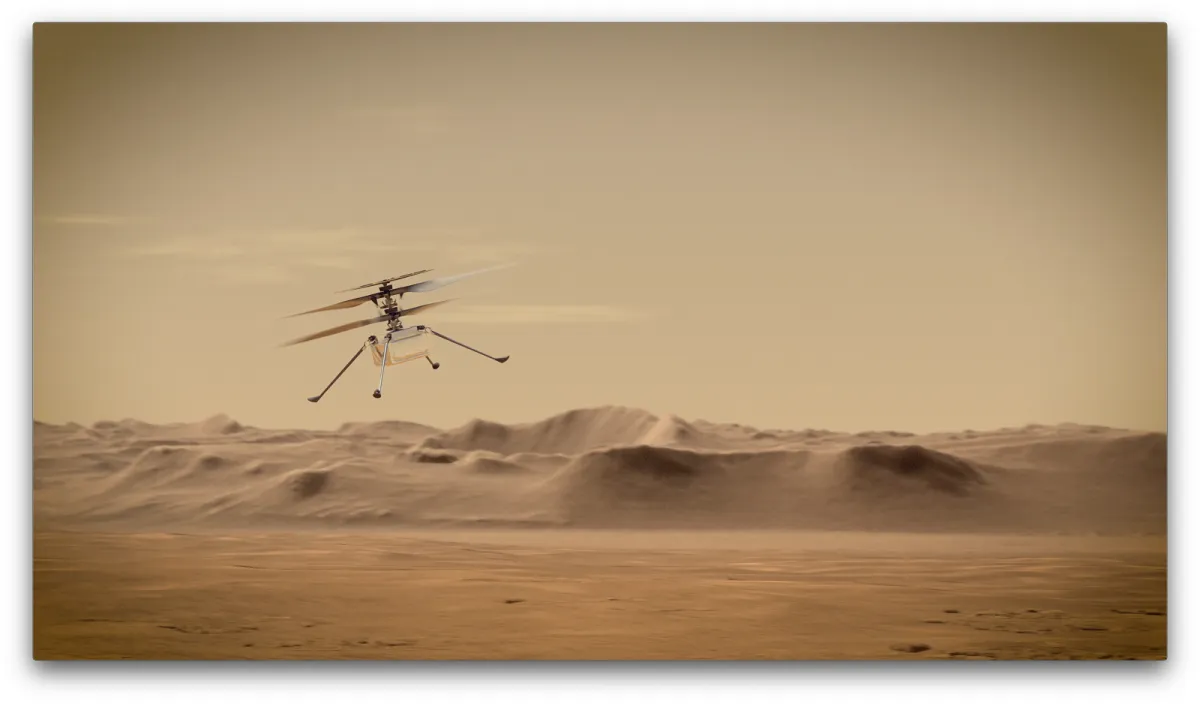 How the First Helicopter on Mars Uses Off-the-Shelf Hardware and LinuxThenewstack
 runc container breakout vulnerabilities: A technical overviewCncf
 Physician Marketing: How to Grow Your PracticeHeygen
 How do I use the latest npm version for my Vercel Deployment?Vercel
