
Secure your build workflow on Bitbucket Pipes with Snyk
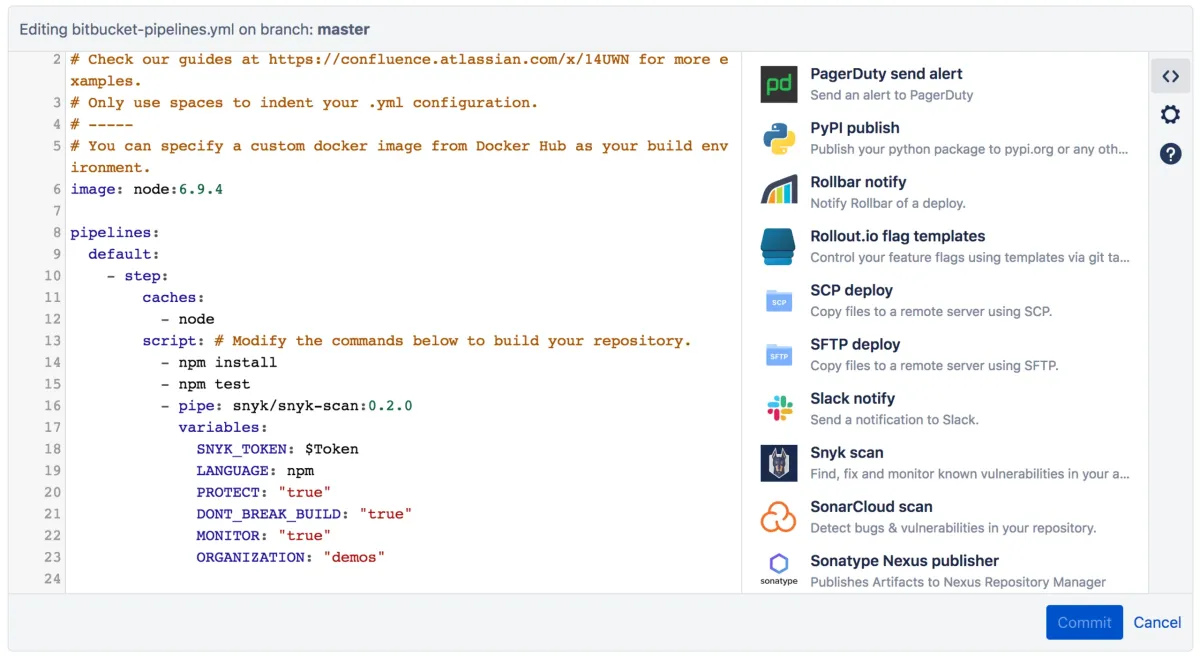
Snyk now integrates with Bitbucket Pipes, which allows Bitbucket users to secure their continuous integration/continuous delivery (CI/CD) workflow by finding, fixing and monitoring open-source vulnerabilities (vulns) in their application or docker image dependencies.
 How to verify and secure your Mastodon accountSnyk
Snyk in 30: Open source security for Atlassian Bitbucket CloudSnyk
What is a Container Registry security?Snyk
10 best practices to containerize Node.js web applications with DockerSnyk
Vulnerability assessmentSnyk
Weaponizing AI Coding Agents for Malware in the Nx Malicious Package Security IncidentSnyk
 How we grew Mintlify by doing things that don't scaleMintlify
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 WooCommerce: App spotlightZapier
 Get email alerts for Facebook Messenger messagesZapier
 Grafana Is Not Worried About AWS CommercializationThenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Real Go Projects: SmartTwitter and web.go - The Go Programming LanguageGo
Go Concurrency Patterns: Pipelines and cancellation - The Go Programming LanguageGo
 Building an RL theorem-proving workflow on ModalModal
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
 Creating an AI Summary App with Next.js | Vercel AcademyVercel
 The Anatomy of shadcn/ui ComponentsVercel
 Build Your Own PluginVercel
 Rolling out a new featureVercel
