
Snyk finds 200+ malicious npm packages, including Cobalt Strike dependency confusion attacks
Snyk recently discovered overt 200 malicious packages in the npm registry. While we acknowledge that vulnerability fatigue is an issue for developers, this article is not about the typical case of typosquatting or random malicious package.
 The Best Video Editing Software in 2026 (Including Free Options)Zapier
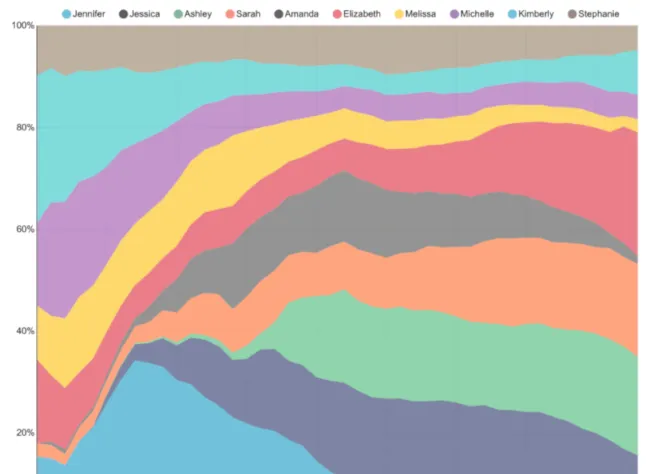 Explore and Visualize Data the Apache Superset WayThenewstack
 Godoc: documenting Go code - The Go Programming LanguageGo
Go.dev: a new hub for Go developers - The Go Programming LanguageGo
 Managing dependencies - The Go Programming LanguageGo
 Docker Desktop 4.23: Updates to Docker Init, New Configuration Integrity Check, Quick SearchDocker
 Capturing Logs in Docker DesktopDocker
 Docker Networking Drivers - Details and Use CasesDocker
 12 Best Uberduck Alternatives for AI Text-to-Speech GenerationHeygen
 Top 5 Youtubers That Will Teach You LangChainDeepgram
 Understanding Redis Enterprise Software Support PackagesRedis
 Google Workspace automationZapier
 Introducing Dependency Divergence GitHub ActionSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
