
So, you think your CI/CD environment is secure?
This post, co-written by Weaveworks and Snyk, explains how by using a GitOps continuous integration (CI)/continuous delivery (CD) pipeline combined with good security practices improves the overall security of your development workflow to Kubernetes.
 How to verify and secure your Mastodon accountSnyk
What is a Container Registry security?Snyk
10 best practices to containerize Node.js web applications with DockerSnyk
Vulnerability assessmentSnyk
Weaponizing AI Coding Agents for Malware in the Nx Malicious Package Security IncidentSnyk
Using Snyk reporting for data-driven securitySnyk
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
 Config and Secret environment variablesVercel
 Configuration and settingsOpentelemetry
 Linux and Cloud Native Security: AlmaLinuxThenewstack
 4 Ways to Get Your Code Back in Shape After Black FridayThenewstack
 What is Workflow Automation?Datadoghq
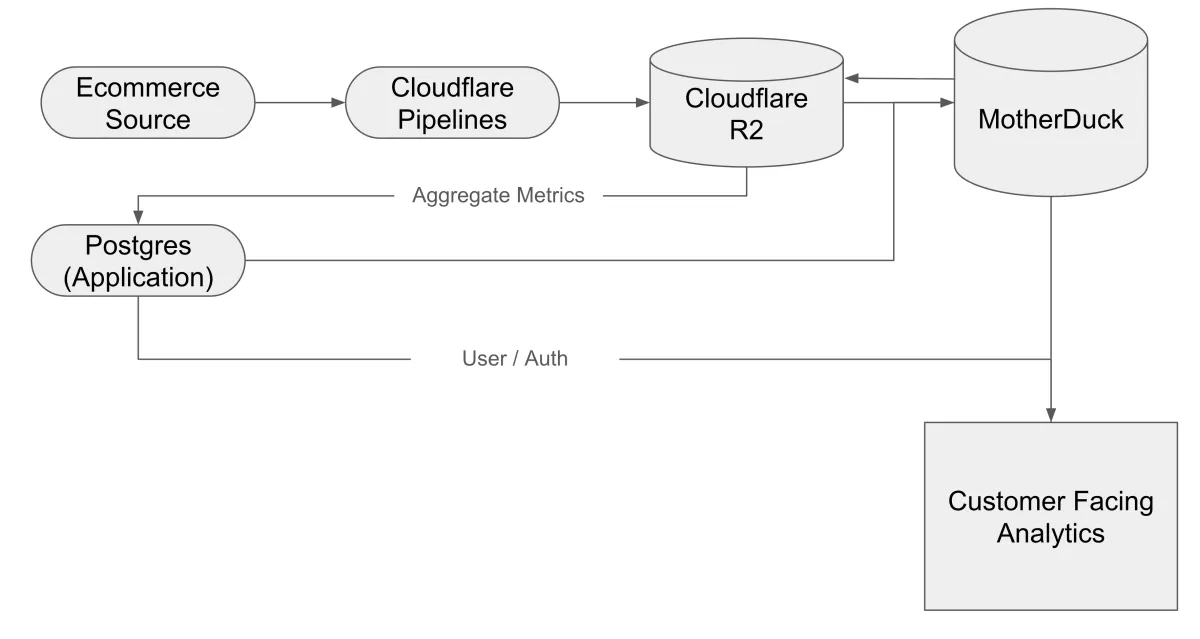 How Layers Slashed Analytics Costs and Gave Every Customer a Private Data WarehouseMotherduck
 Aleph Alpha Selects Cerebras to Build Next-Gen Sovereign AI Models - CerebrasCerebras
 with JupyterLab as a Docker ExtensionDocker
 DockerCon Workshops: Getting Started with Docker, AI/ML, Secure DevelopmentDocker
 Introducing bunny.net Perma-Cache - Permanent CDN CachingBunny
 Introducing MediaCage Enterprise: Simplified Video Security for Creators and BusinessesBunny
