
Stranger Danger: Live hack of how a Log4Shell exploit works
Learn about a recent Stranger Danger live hack where Simon Maple, Field CTO at Snyk, Eric Smalling, Senior Developer Advocate at Snyk, and Micah Silverman, Director of DevSecOps Acceleration discussed the Log4Shell vulnerability and demonstrated how an exploit could work.
 What is a Container Registry security?Snyk
10 best practices to containerize Node.js web applications with DockerSnyk
How to verify and secure your Mastodon accountSnyk
Vulnerability assessmentSnyk
Weaponizing AI Coding Agents for Malware in the Nx Malicious Package Security IncidentSnyk
Using Snyk reporting for data-driven securitySnyk
 Publish changes - MintlifyMintlify
 Video: Building a Live Transcription Badge With Deepgram - Deepgram Blog ⚡️Deepgram
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 SQL is Dead, Long Live SQL: Engineering a Reliable Analytics Agent from ScratchMotherduck
 DockerCon LIVE with theCUBE: Call for Papers is OpenDocker
 GitHub - MintlifyMintlify
 Preview locally - MintlifyMintlify
 Credit pricing - MintlifyMintlify
 How the AI Business World Actually Works: A Startup’s WarDeepgram
 Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot ServiceSocket
 Product updates: Logs v2, live container profiling, and region selection on all plansModal
 Web standards - GlossaryDeveloper Mozilla
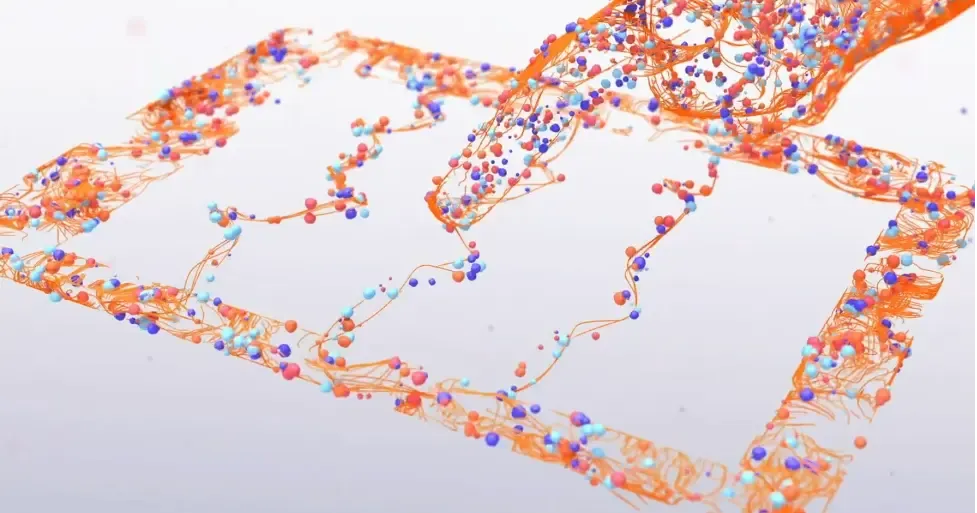 A Big Chip for Big Science: Watching the COVID-19 Virus in Action - CerebrasCerebras
 with JupyterLab as a Docker ExtensionDocker
