
Targeted npm dependency confusion attack caught red-handed | Snyk
Once in a while we encounter a truly malicious package that has a purpose, means, and is production-ready — this is a story about one found in npm: gxm-reference-web-auth-server.
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Anthropic Identifies Biased Reasoning and Recklessness as Drivers of Claude’s PyPI AttackSocket
 Introducing Dependency Divergence GitHub ActionSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 Happy Birthday, Shai-HuludSocket
 Announcing dependency caching for Pulumi DeploymentsPulumi
 Forward Compatibility and Toolchain Management in Go 1.21 - The Go Programming LanguageGo
 How to Protect Your Projects from the Risks of Deprecated npm PackagesSocket
 When "Everything" Becomes Too Much: The npm Package Chaos of 2024Socket
 Popular npm Packages in the keyv and Cacheable Namespaces Compromised in Active Supply Chain AttackSocket
 Supply Chain Attack on Axios Pulls Malicious Dependency from npmSocket
 What Observability Should Do for Your OrganizationThenewstack
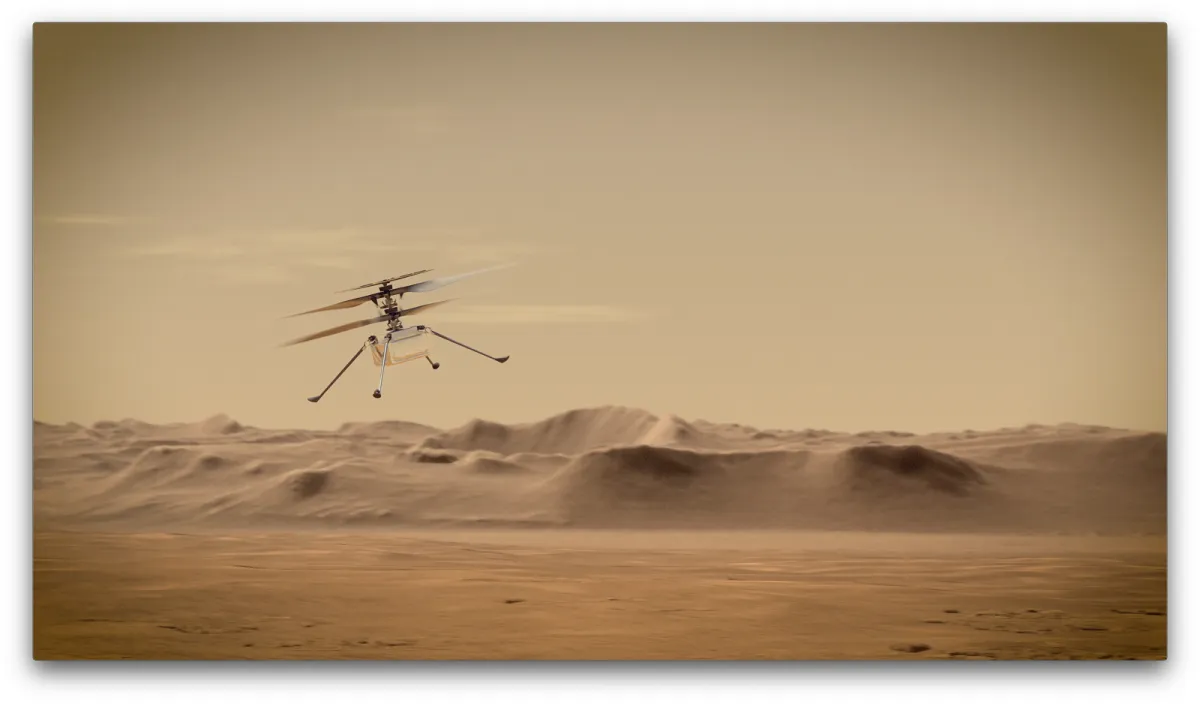 How the First Helicopter on Mars Uses Off-the-Shelf Hardware and LinuxThenewstack
