
TensorLake npm SDK Compromised in ChainDrop Shai-Hulud Credential-Stealing Attack
Tensorlake npm SDK version 0.5.144 was compromised in a ChainDrop / Shai-Hulud attack, delivering credential-stealing malware.
 OpenAPI React Query Codegen Compromised in Mini Shai-Hulud npm Supply Chain AttackSocket
 Popular npm Packages in the keyv and Cacheable Namespaces Compromised in Active Supply Chain AttackSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 Happy Birthday, Shai-HuludSocket
 Re-Enabled GitHub Actions Expose Thousands of Repositories to Mini Shai-HuludSocket
 Supply Chain Attack on Axios Pulls Malicious Dependency from npmSocket
 Pulumi ESC Table Editor Now Supports Dynamic Credential and Secret IntegrationsPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 The App Engine SDK and workspaces (GOPATH) - The Go Programming LanguageGo
 Creating an AI Summary App with Next.js | Vercel AcademyVercel
 Anthropic Identifies Biased Reasoning and Recklessness as Drivers of Claude’s PyPI AttackSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 GlassWorm Loader Hits Open VSX via Developer Account CompromiseSocket
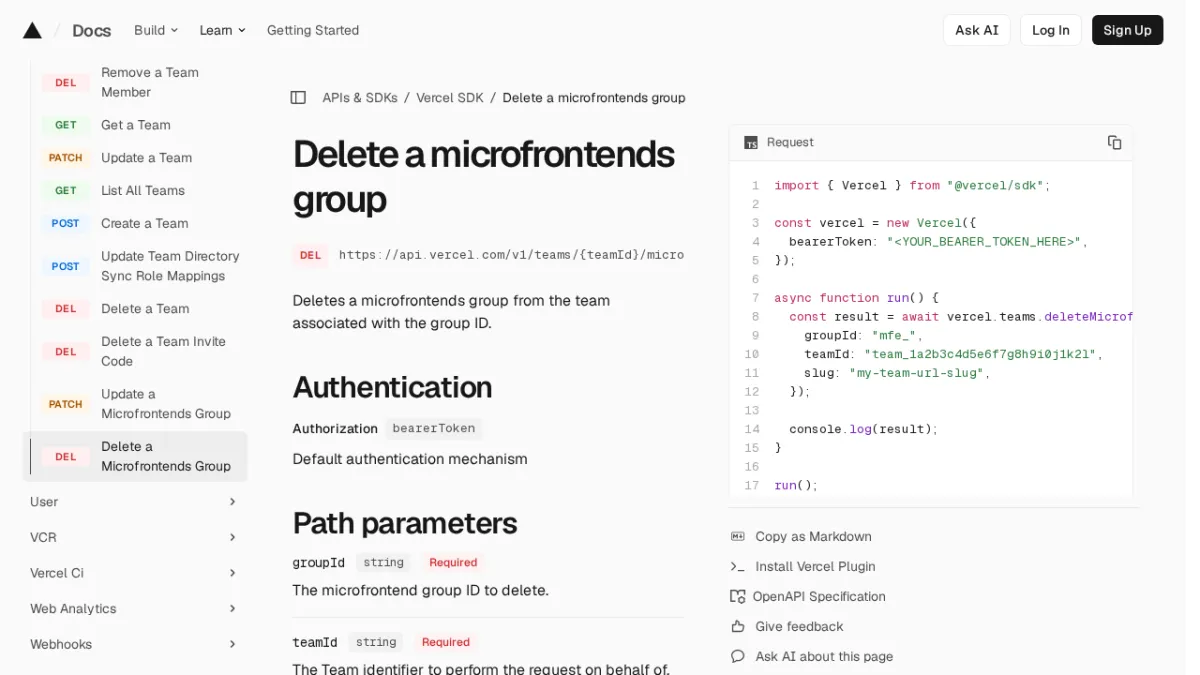 Delete a microfrontends group | Vercel SDKVercel
 Introducing Vercel AI SDK 3.2Vercel
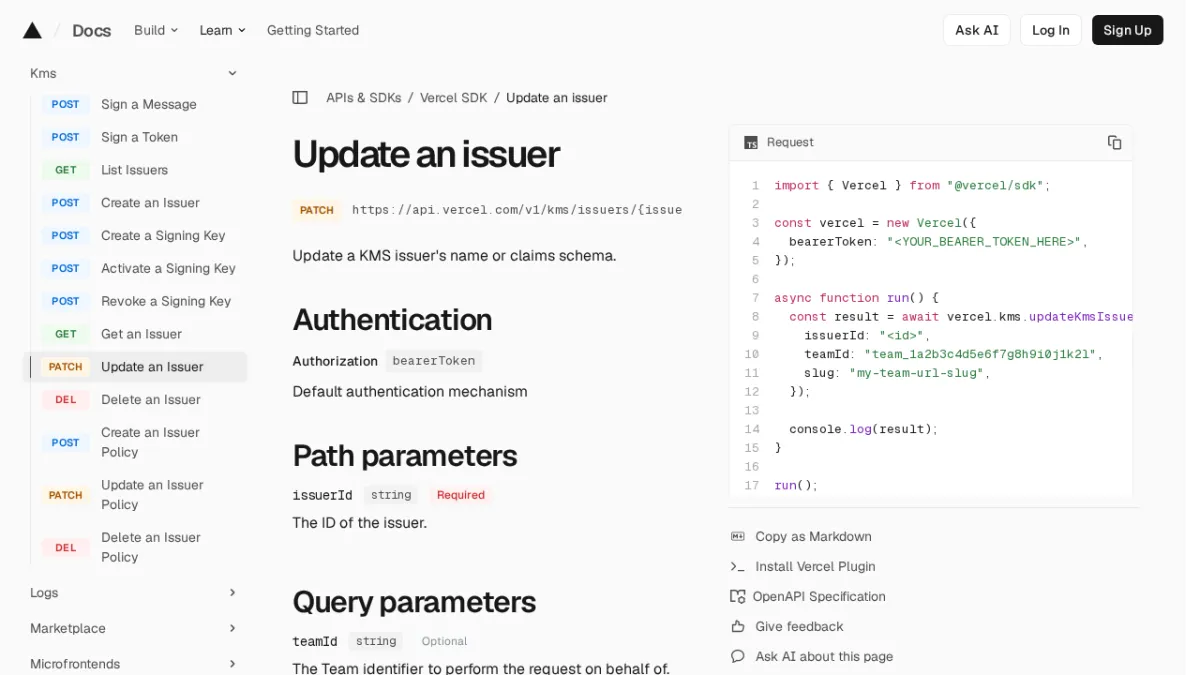 Update an issuer | Vercel SDKVercel
 Large-Scale GitHub Actions Abuse Powers a Distributed cPanel and WHM Exploitation CampaignSocket
 How to Protect Your Projects from the Risks of Deprecated npm PackagesSocket
 When "Everything" Becomes Too Much: The npm Package Chaos of 2024Socket
 PolinRider Spreads Through Compromised GitHub Accounts and PackagistSocket
